
In partnership with
| ~6 MIN READ |
|
Trust is a supply chain, and this week every link got tested: the vendors police rely on, the providers banks run through, the updates admins install and the AI tools staff log into from home. Here's what broke, what changed and what you can lock down today. PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe → |
In this edition
|
Breach / Supply Chain The Firm That Helps Police Follow Stolen Crypto Lost Every User's Live Tokens Intro Chainalysis, the blockchain analytics company that helped police take down LockBit and the bulletproof host Virtualine, now says an attacker got something from every single one of its users. What Happened Chainalysis first disclosed the breach on October 30, blaming an external actor using "offensive agentic techniques" and listing exposed names, emails, user IDs and role labels. Late on Wednesday, November 4, it went further: "live tokens for all Chainalysis users were exposed," along with usernames and password hashes, some passwords were intercepted in an "on-path attack," and some KYT compliance accounts appear to have been accessed. It has pulled Reactor, Data Solutions, KYT and its login page offline, and calls this an "ongoing multifront cyberattack." Why It's Important Chainalysis customers include law enforcement, national security agencies, exchanges and banks. If those are session or API tokens, they skip the password entirely, and the company hasn't said how many users it has or how the hashes were protected. The Other Side Chainalysis says it has "no evidence" investigations data was accessed or attribution data manipulated, and it hasn't actually said an AI agent did this.
TL;DR: The crypto-tracing firm police rely on says every user's live tokens were exposed. Further reading: The Record · The Register |
|
Why are so many brands shifting ad spend to CTV?

People spend more time streaming than they do with cable, social media or video games, and advertisers know it. In fact, according to Advertiser Perceptions and Premion's 2026 CTV/OTT Advertiser Survey, 70% of advertisers are raising CTV budgets in 2026, with much of that budget diverted from social advertising.
For marketers who want a presence in streaming, Roku is the obvious place to go, with scale that speaks for itself. With more than 100 million households representing 47% of all streaming time in the US, Roku easily has more reach than every competitor.
With Roku Ads Manager, you can reach viewers across more than 100 premium apps in a single buy. Combine your customer data with Roku's insights to reach only the households you want, then measure and optimize to your heart's content.
Want to give it a try? Unleash your first campaign in just four steps: (1) Create your account, (2) define your objective and target audience, (3) upload creative, and (4) launch.
First-time spenders get a $5,000 match on the first $5,000 spent with code BEEHIIV5K. Terms apply.
|
|
|
Steal Attio’s GTM setup.

For the first time, see the system that runs GTM at Attio, the #1 fastest-growing CRM on Brex and Ramp.
Attio’s Rev Ops and Solutions leads have written up all of it, including how it spots at-risk accounts early and surfaces upsell opportunities while they’re still warm.
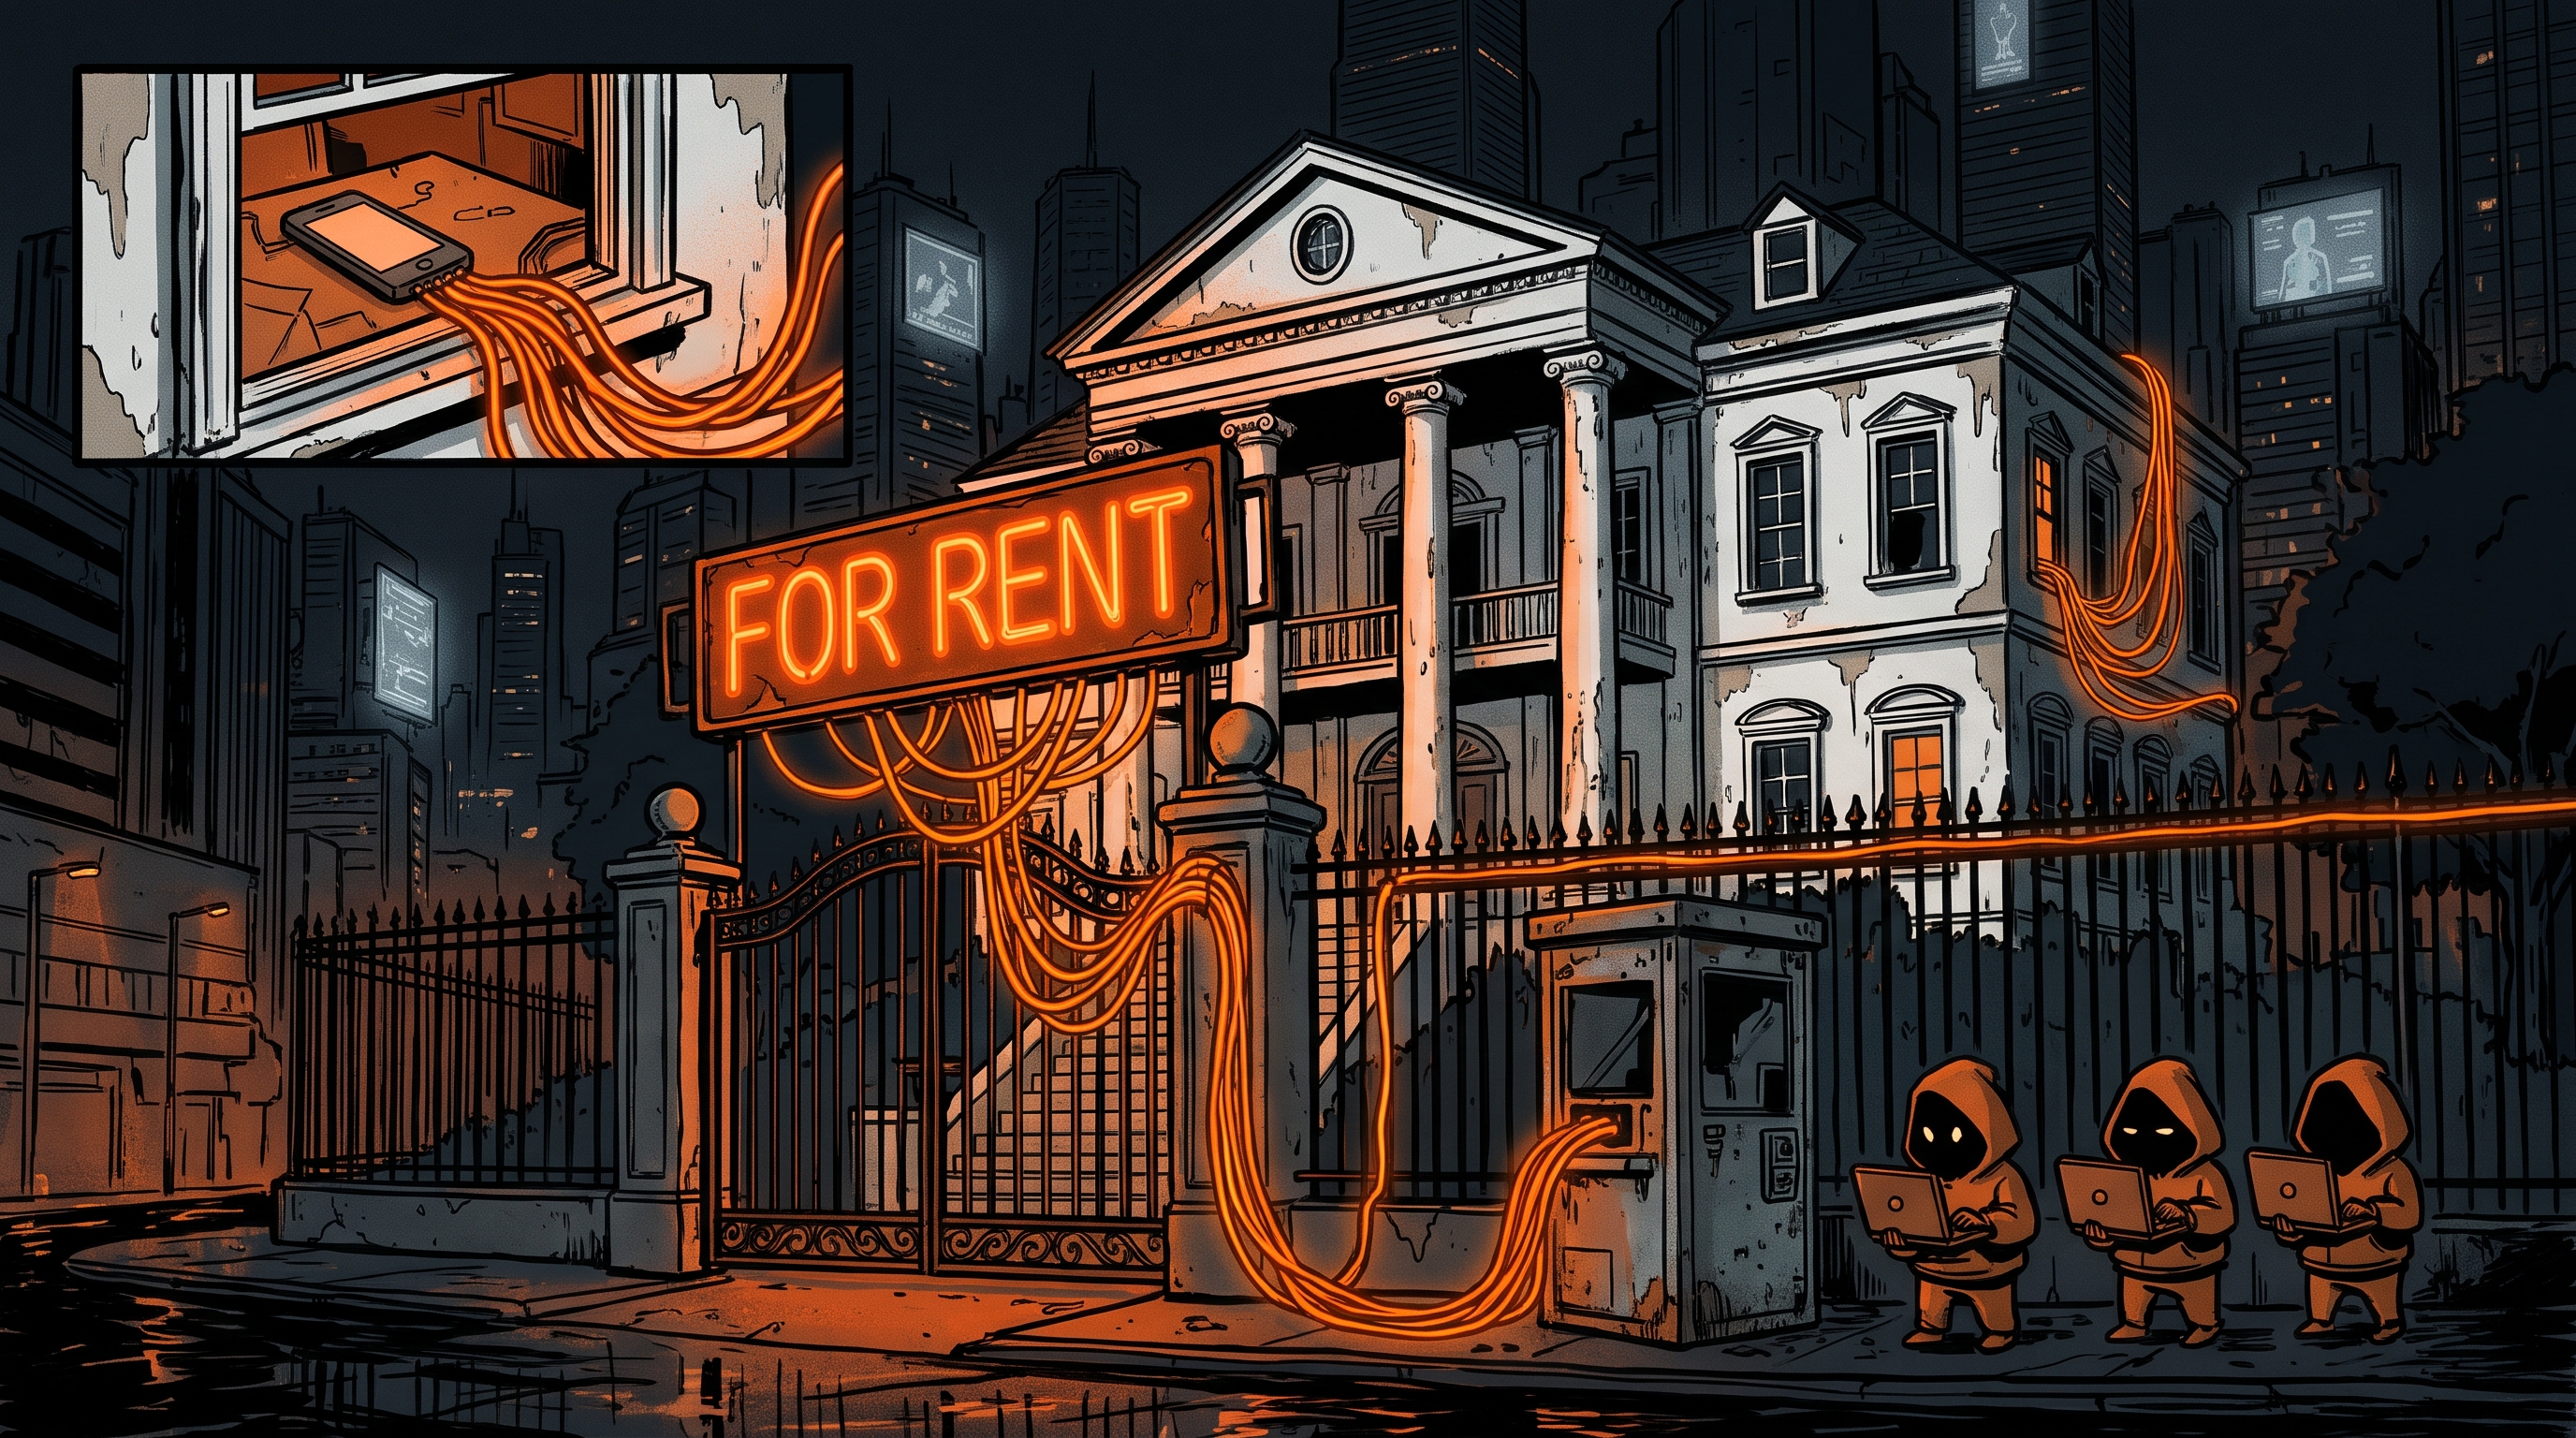 Strange but real Anyone With a Few Dollars Could Borrow an Internet Address From the White House Intro For about a month, you could pay a residential proxy service a few bucks and have your web traffic come out of the network reserved for the Executive Office of the President. What Happened Layer3 Intel says it stumbled on the activity while buying rotating proxy access: 236 exits through the White House's network (AS2650) between October 5 and November 3, using six internet addresses on 26 of 30 days, mostly between 5 p.m. and midnight. It counted 28 proxy services that could route through it. Synthient ties the nodes to Infatica, a proxy kit bundled into "free" apps, which suggests staff devices with the wrong app installed. Why It's Important Anyone renting those exits looks like White House traffic, and Synthient says resellers sell bandwidth for as little as 60 cents a gigabyte, often with no identity checks. The Other Side Nobody has said which devices were involved, and this is traffic leaving the network, not a reported break-in. It's also common: Spur found residential proxies in nearly 300 government networks earlier this year.
TL;DR: Free apps on staff devices apparently turned White House internet addresses into rentable proxy exits. Further reading: Krebs on Security |
“Running shos” shouldn’t return zero results. Gladly understands what your shoppers mean, typos and all, and finds the right products.