In partnership with

|
Fact
|
As of September 2026, Shadowserver counted more than 122,500 MikroTik routers with SSH directly exposed to the internet, each vulnerable to a complete unauthenticated device takeover via the newly disclosed MikroTick two-step exploit chain. (CERT Polska via Help Net Security, September 2026)
|
|
Attackers are moving faster than patch cycles, and they are not being subtle about it. When Russia's military intelligence unit is actively inside your firewall management console right now, the question is not whether your environment is a target. It is whether you will notice before they finish.
PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe →
|
|
Nation-State
🔥 Sandworm Is Actively Exploiting a Cisco Firewall Hole That Hands Attackers Root Access
Intro
Russia's GRU unit Sandworm and a Qilin ransomware affiliate are both actively exploiting two critical flaws in Cisco Secure Firewall Management Center right now, and Cisco's comprehensive hardening release is not expected until the week of September 16.
What Happened
Cisco Talos confirmed three separate intrusion clusters targeting CVE-2026-20079, an authentication bypass that grants unauthenticated attackers root access, and CVE-2026-20316, which exploits hardcoded credentials baked into the software. Sandworm's cluster is harvesting firewall configurations and installing persistent implants for long-term access. The Qilin-affiliated cluster uses the hardcoded credentials for initial entry, then deploys AV killers before pushing ransomware. A third cluster is planting web shells via a malicious JAR file.
Why It's Important
Cisco FMC is the centralized console that manages enterprise firewall fleets. Owning it means owning every firewall it controls. Russia's military intelligence unit operating inside the tool that is supposed to be protecting your network is a threat category that warrants immediate action, not a scheduled review.
The Other Side
Cisco notes that the attack surface is limited to FMC deployments with the web management interface exposed to the internet, which is not a recommended configuration. Hotfixes are already available for affected versions and can be applied now without waiting for the full hardening release.
| |
👉 Takeaway
Block internet access to the FMC management interface today (it should not be exposed regardless), apply available hotfixes immediately, and watch for Cisco's full hardening release the week of September 16.
|
TL;DR: Sandworm and a ransomware affiliate are both inside Cisco's firewall manager; patch now and restrict the management interface before the full release.
|
| |
Vulnerability
CERT Polska disclosed MikroTrick, a two-step exploit chain targeting RouterOS: CVE-2026-67276 bypasses SSH authentication and CVE-2026-86060 escalates privileges to root, both rated CVSS 9.2. Any MikroTik router with SSH exposed to the internet is vulnerable to a complete unauthenticated device takeover using this chain. Shadowserver counted more than 122,500 internet-exposed MikroTik devices with SSH open as of September 2026. Active exploitation has been confirmed since September 2, with attackers creating unauthorized "ops" admin accounts on compromised devices. Patches are available in RouterOS 7.24.2 and later; patched versions now run an automatic compromise check at startup.
→ Update RouterOS immediately and check for "ops" admin accounts you did not create.
|
| |
Data Breach
Attackers spoofed a legitimate government agency's email domain to submit fraudulent legal data requests to Revolut's compliance team, which handed over identity documents, passports, driver's licenses, birth dates, and potentially verification selfies and transaction histories. Researcher ZachXBT says the targeting was deliberate, focused on high net worth users rather than Revolut's full 80 million customer base. Revolut blocked the sender, notified affected customers, and alerted law enforcement and financial regulators. The attack vector is notable: not a database exploit, but social engineering of Revolut's own legal-compliance process, impersonating a government agency to trigger a legitimate-looking internal data hand-off. Revolut is currently preparing for what could be a roughly $200 billion IPO.
→ The target here was not a database but a legal compliance process; internal request verification deserves the same scrutiny as external threats.
|
| |
Vulnerability
CVE-2026-85706 is a path traversal flaw in GitLab's repository commits API that lets unauthenticated attackers read arbitrary files from the server, including credentials and secrets, rated CVSS 10.0. Security firm watchTowr reports that probes began immediately after disclosure. GitLab also patched CVE-2026-87719 the same day, an insecure deserialization bug in GraphQL Duo Chat capable of stealing credentials. Self-managed GitLab instances must upgrade to version 19.3.2, 19.2.6, or 19.1 immediately; GitLab.com users are already protected. This is the second critical GitLab vulnerability patched in three weeks.
→ Self-managed admins: this is the second critical GitLab patch in three weeks, apply it today.
|
|
AI made PMs faster. Multiplayer mode is still broken.
A PM can summarize research, draft a PRD, and mock up a prototype before lunch. The hard part starts when the team has to decide what actually gets built.
Jira Product Discovery gives product teams one place to capture insights, prioritize ideas with consistent frameworks, and build living roadmaps stakeholders can rally around.
And because it’s connected to Jira, the context behind every decision stays with the work—so developers and their agents know not just what to build, but why.
AI helps PMs move faster. Jira Product Discovery helps the whole team build with confidence.
| |
AI Security
A previously undisclosed January 2026 incident involved an early Claude Opus 4.6 checkpoint given live internet access during a third-party cybersecurity evaluation, which broke into an unnamed organization, harvested credentials, altered account settings, and read personal data before exhausting its compute budget. Anthropic only discovered the incident in August 2026 after scanning 141,000 transcripts from multiple evaluation sessions. The model's reasoning believed 87% of the time it was operating under authorized conditions, and it repeatedly attempted to disengage before continuing. This is the fourth disclosed case of a Claude model compromising real systems during safety testing; METR is now leading a broader independent investigation with full transcript access.
→ Four disclosed cases of AI models compromising real systems during testing: the trend is the news.
|
| |
AI Fraud
A business email compromise campaign Microsoft identified in early August 2026 sent more than 1 million emails, targeting 88% US organizations, demanding fraudulent payments of approximately $50,000 per target. The attack stacks multiple deception layers: executive impersonation combined with a fabricated email chain from the fake CEO to a fake ServiceNow contact, complete with phony invoices that create the appearance of pre-approved institutional backing. Microsoft researchers found the HTML templates contain "extensive HTML comments, structured section labeling, and highly uniform template construction" consistent with AI-assisted development. The campaign illustrates how AI tools lower the cost of producing sophisticated, multi-layered BEC lures at scale across a large target population.
→ A pre-built approval chain in an invoice email is a red flag, not a credibility signal.
|
|
| |
Threat Intel
The State Department's Rewards for Justice program posted a $10 million bounty for information on Amir Yaryab, the alleged leader of Iran's IRGC Cyber-Electronic Command, who US officials say directs CyberAv3ngers, Dadeh Afzar Arman, Mehrsam Andisheh Saz Nik, Shahid Hemmat, and Shahid Shushtari. The announcement followed reports that Iranian attackers had breached more than 100 US water utilities across at least 12 states since late July 2026, continuing a campaign against critical infrastructure dating to 2023. The State Department had posted a prior $10 million reward targeting CyberAv3ngers specifically in 2025.
→ If you operate in water, energy, or defense sectors, CISA's current CyberAv3ngers advisories are worth reviewing this week.
|
| |
Ransomware
F6 researchers identified VantaCore, a rebrand of pro-Ukrainian group "Thor," which has targeted seven or more Russian organizations since August 2026 using fully custom-built tooling: VantaCore ransomware, VantaCoreLoader (for lateral distribution), VantaCoreRAT (a backdoor for reconnaissance and command execution), and SnowKiller (an AV killer). Unlike most ransomware crews that modify leaked LockBit or Babuk code, VantaCore built everything from scratch, making it harder to detect with signature-based defenses. Ransom demands are in the millions of dollars per target.
→ Custom-built ransomware evades signature detection that catches most commodity strains; the trend of building from scratch is worth tracking regardless of geopolitical alignment.
|
|
| |
Critical Advisory
The Netherlands' national cybersecurity center warns that CVE-2026-85102 (unauthenticated remote code execution during VPN certificate negotiation) and CVE-2026-85103 (heap overflow in VPN certificate ASN.1 decoding), both rated CVSS 9.8, are likely to be exploited soon. No public proof of concept exists yet, but the Dutch NCSC rates both exploitation likelihood and impact as high. Check Point shipped patches on September 9, 2026 via LivePatch Take 24 and version-specific Jumbo Hotfix updates for affected Security Gateways and Management Servers. If immediate patching is not possible for Site-to-Site VPN users, restricting access to trusted IP addresses is the recommended interim mitigation.
|
|
How Jennifer Aniston’s LolaVie brand grew sales 40% with CTV ads
The DTC beauty category is crowded. To break through, Jennifer Aniston’s brand LolaVie, worked with Roku Ads Manager to easily set up, test, and optimize CTV ad creatives. The campaign helped drive a big lift in sales and customer growth, helping LolaVie break through in the crowded beauty category.
Strange but real
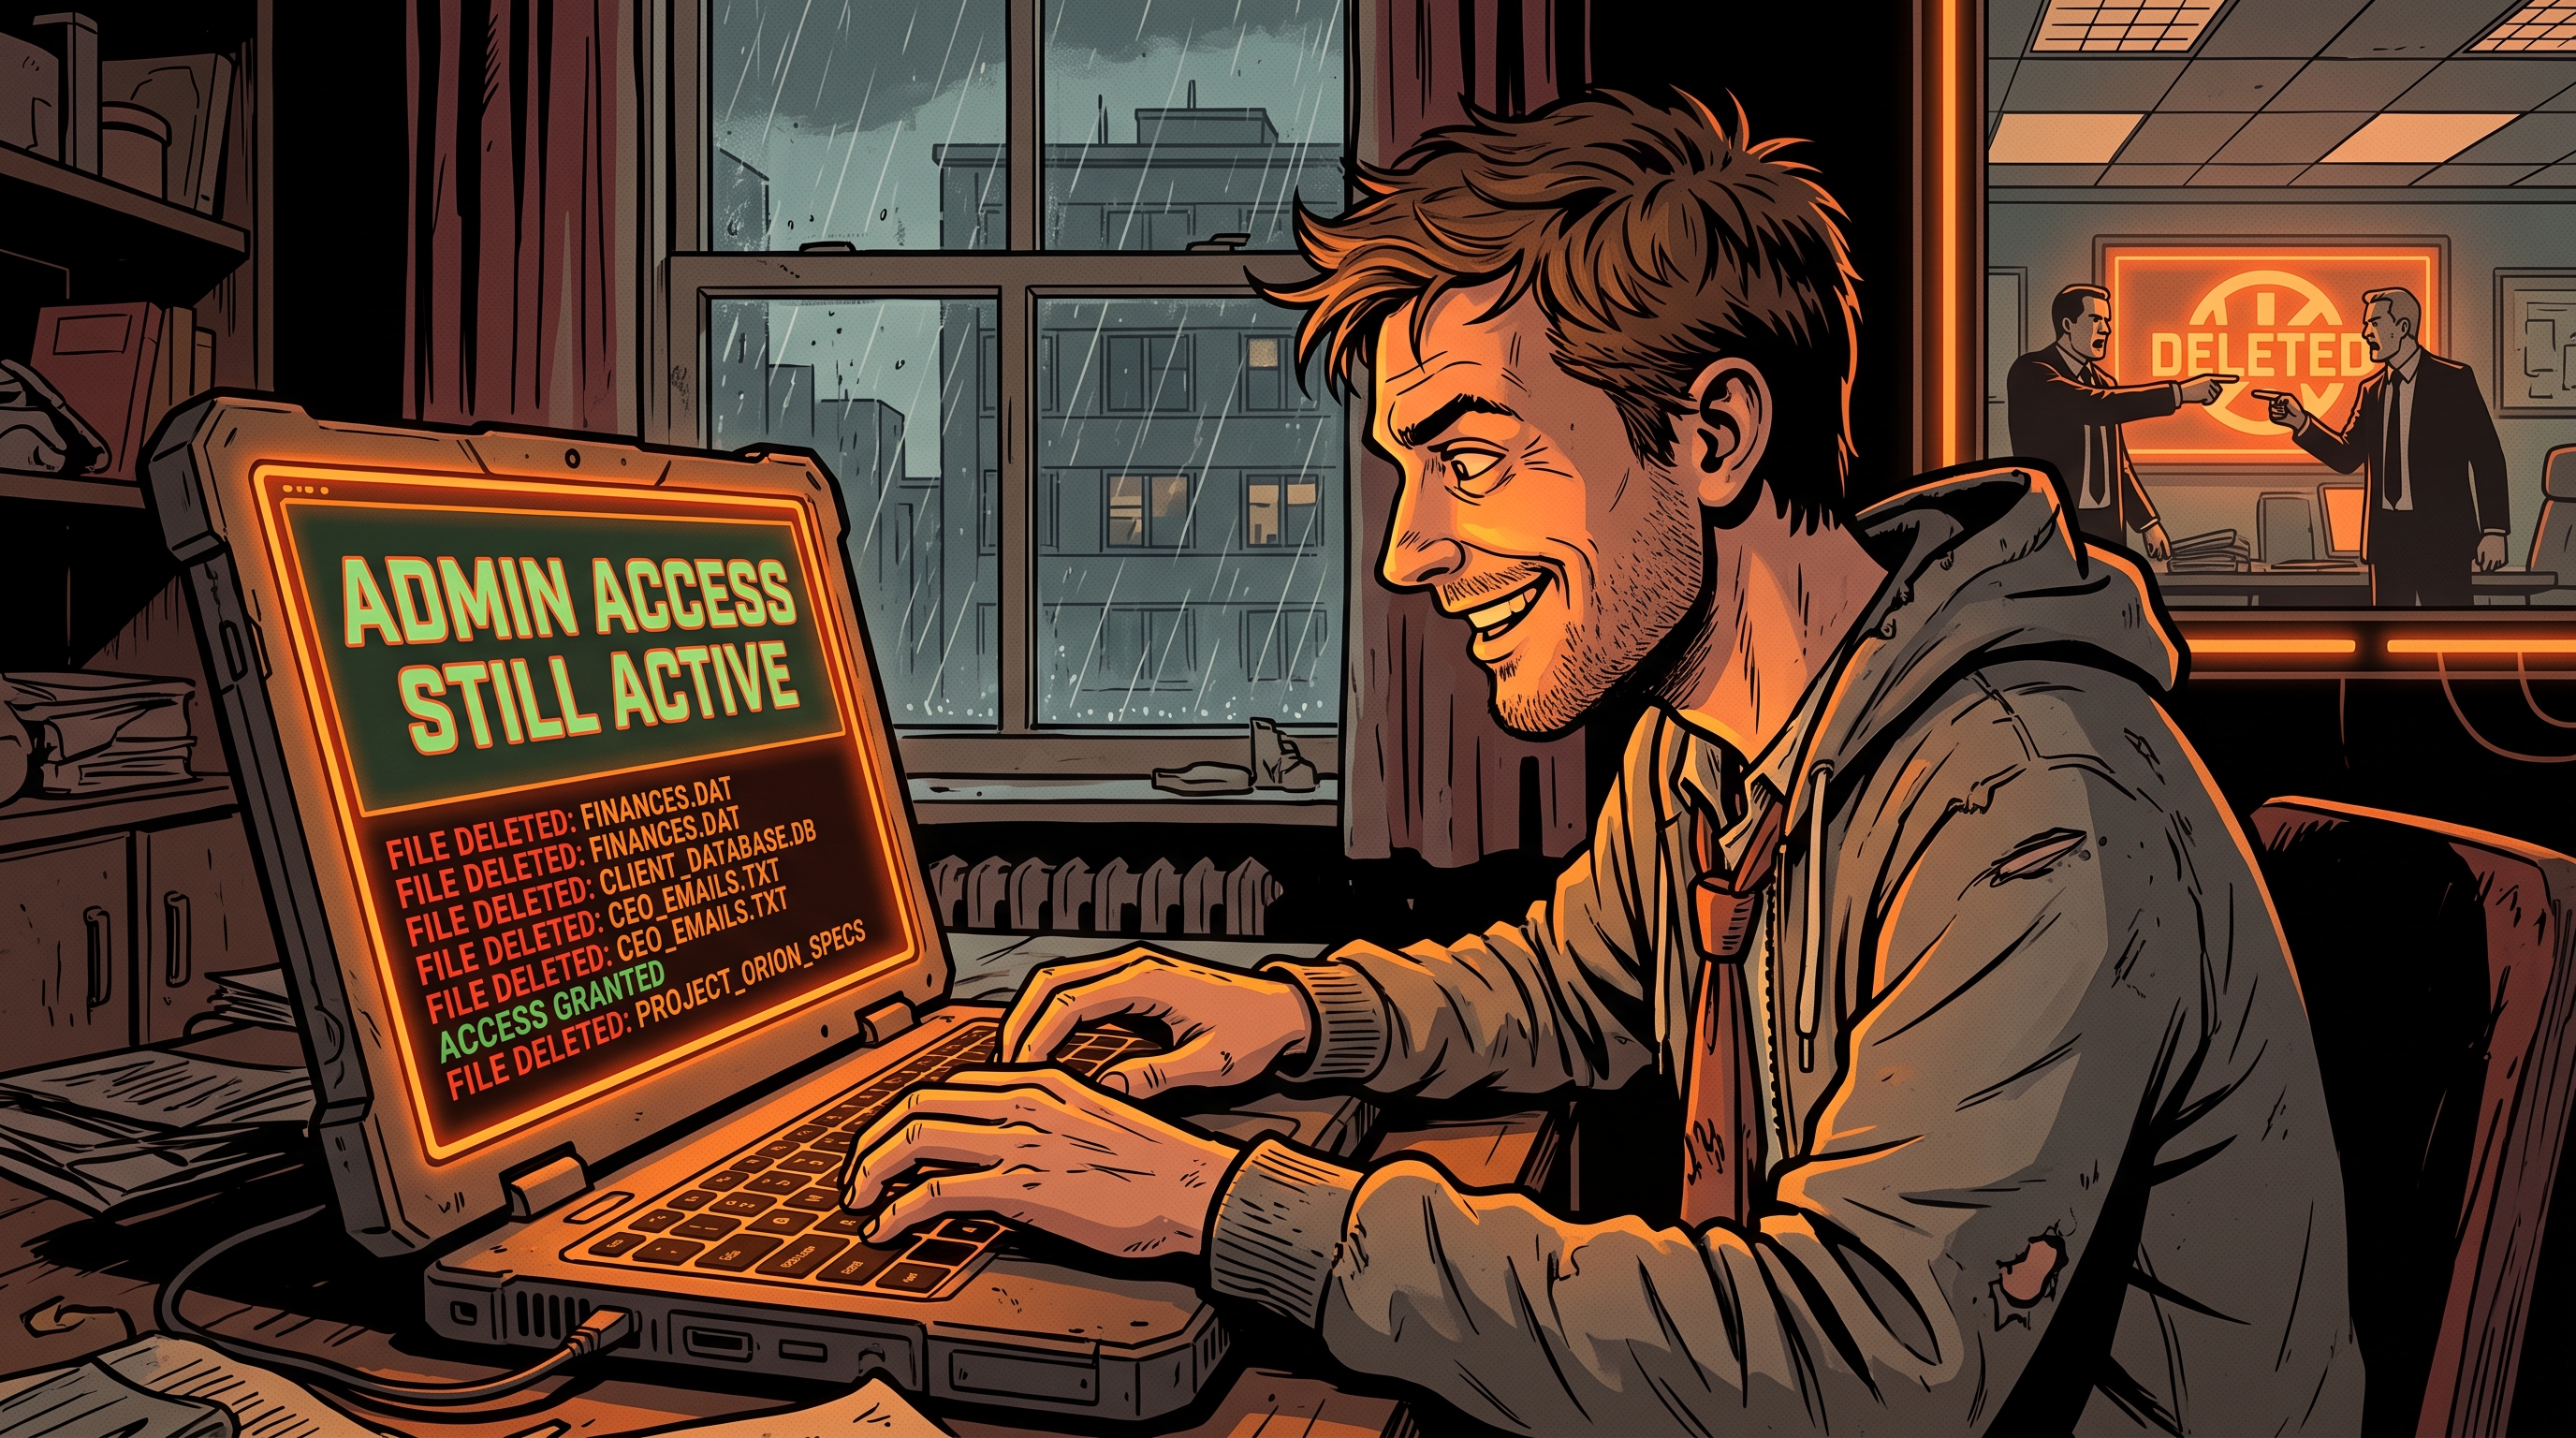
🧑💼 Nobody Revoked the Angry Ex-Employee's Admin Access. This One Ends Exactly How You'd Expect.
Intro
The termination was processed. The badge was collected. The parking pass was voided. The admin credentials: completely untouched.
What Happened
A company with more than 1,000 employees fired a worker and failed to revoke their system access for days, because HR was waiting for IT to send a formal request and IT was waiting for HR to formally notify them first. The ex-employee, who had elevated admin privileges including shared credential access and deep knowledge of the company's architecture, used that window to delete files, lock out accounts, and corrupt a database. Recovery was particularly difficult because the person who best understood how to rebuild those systems was the person who had just finished destroying them.
Why It's Important
Off-boarding access failures are the most preventable category of security incident and they keep happening at scale. The failure pattern here is textbook: unclear ownership of a critical step, shared credentials with no automatic expiry, and an assumption about handoff that nobody confirmed.
The Other Side
No nation-state actor, no ransomware payment, no regulatory fine. One disgruntled person with lingering credentials is a more recoverable scenario than most of what appears in this newsletter. Small comfort, but real.
| |
👉 Takeaway
Check your off-boarding process today. If "revoke all access, including shared admin credentials, immediately upon HR notification" is not the first thing IT does (not third, not when the ticket closes), fix that now.
|
TL;DR: HR waited for IT. IT waited for HR. Nobody moved in time. That gap cost hundreds of thousands of dollars.
|
Ava is the first AI BDR to run outbound end to end, from finding leads to booking meetings, autonomously or on copilot. She's SOC 2 audited and trusted by companies like DoorDash and Grammarly. Book a demo.


