In partnership with

~7 MIN READ
FACTMultiple security firms flagged LiteLLM's poisoned 1.107.0 release within six minutes of publication, yet the bad PyPI wheels stayed live for about an hour and 40 minutes. (BleepingComputer, October 2026)
The Signal
 
Attackers keep skipping the front door for the suppliers and platforms that already have a key, while courts and cops try to send the bill.

PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe →

In this edition
 📌 Big Cyber News
 🚨 Can't Miss
 🤖 AI in Cyber
 🏛️ Privacy, Power & Policy
 🛠️ Tools & Tactics
 🧪 Strange Cyber
📌 Big Cyber News
 
Ransomware / Critical Infrastructure
SafePay Went After 600 Critical Infrastructure Orgs Without a Single Affiliate
Intro
Most ransomware gangs rent their malware to affiliates. SafePay does its own dirty work, and the feds say it has been busy.
What Happened
A joint advisory (AA26-293A) from CISA, the FBI, the Secret Service and police in Germany and the UK says SafePay has hit at least 600 organizations across multiple critical infrastructure sectors since August 2024, in North America, South America, Europe and Australia. The private crew steals data before encrypting and gets in through exposed credentials, brute force, phished accounts, VPN access (often from Mullvad VPN addresses) and scripts that exploit edge-device CVEs. Then it deletes shadow copies and resets the NAS devices holding backups.
Why It's Important
CISA calls SafePay "one of the most active ransomware groups," and it has reportedly filled the gap LockBit and BlackCat left behind. Its leak site lists only victims who don't pay, so 600 is a floor.
The Other Side
Nothing in this playbook is new. Stolen passwords, unpatched edge gear and reachable backups are problems most organizations already know they have.
 
👉 Takeaway
Patch the VPN, firewall and edge flaws on CISA's KEV list first, enforce MFA, restrict admin tools, and make sure someone with admin rights can't wipe your backups. Then load the advisory's IOCs into your detections.
TL;DR: A ransomware crew with no affiliates has hit 600+ critical infrastructure orgs through doors defenders already know about.
Further reading: BleepingComputer
🚨 Can't Miss
 
 
Zero-Day
Arista says attackers are exploiting CVE-2026-114625, a SQL injection in VeloCloud Orchestrator that lets any logged-in user with basic privileges become a "superuser operator." It's the fourth actively exploited Arista zero-day this year. Fixes are in 5.2.3.18, 6.1.3.10 and 6.4.2.12, and attack traffic came from 74.82.197.86 and 38.54.50.151.
→ Patch, block those IPs, and lock the web interface to admin networks.
 
Cloud Platform
Railway disclosed October 21 that an unauthorized party may have accessed encrypted environment variables, "and, in some cases, obtained the decrypted contents." Those hold API keys and database credentials. Researcher Taylor Monahan says crypto wallets with keys stored on Railway were drained at least two hours before the disclosure. Railway thinks it's part of a campaign against platform companies aimed at AI inference providers.
→ Railway customers: rotate every environment variable now.
 
Law Enforcement
Operation Serengeti III ran this summer across 20 African countries plus the US, disrupting more than 10,000 malicious networks and identifying just under 66,000 victims with losses above $385 million. Uganda arrested 365 foreign nationals running call centers that pitched fake investments to pensioners in Asia. Angola seized more than 2,000 crypto mining devices.
→ Fraud call centers are global, and so are their marks.

How Jennifer Aniston’s LolaVie brand grew sales 40% with CTV ads

For its first CTV campaign, Jennifer Aniston’s DTC haircare brand LolaVie had a few non-negotiables. The campaign had to be simple. It had to demonstrate measurable impact. And it had to be full-funnel.

LolaVie used Roku Ads Manager to test and optimize creatives — reaching millions of potential customers at all stages of their purchase journeys. Roku Ads Manager helped the brand convey LolaVie’s playful voice while helping drive omnichannel sales across both ecommerce and retail touchpoints.

The campaign included an Action Ad overlay that let viewers shop directly from their TVs by clicking OK on their Roku remote. This guided them to the website to buy LolaVie products.

Discover how Roku Ads Manager helped LolaVie drive big sales and customer growth with self-serve TV ads.

The DTC beauty category is crowded. To break through, Jennifer Aniston’s brand LolaVie, worked with Roku Ads Manager to easily set up, test, and optimize CTV ad creatives. The campaign helped drive a big lift in sales and customer growth, helping LolaVie break through in the crowded beauty category.

🤖 AI in Cyber
 
 
AI Agents
Microsoft pins the ConnectWise Cloud Backup supply chain attack on Storm-0940, a China state-aligned group using ARTEX, an agentic AI pentest framework. The agents fired up to 2,900 sign-in attempts per minute, and on October 15 took over ConnectWise cloud app identities to reach customer environments. In several cases, under three hours passed between first targeting and privileged access.
→ Check OAuth apps for new credentials and privileged role changes.
 
Supply Chain
Attackers who hijacked the AI gateway's pipeline October 21 pushed 1.107.0 with three extra files that run whenever Python starts, including when you launch it to investigate. The malware grabs cloud, Kubernetes, CI/CD, SSH and AI provider credentials plus browser logins, then polls a GitHub pointer hourly for more code. It gets about 92 million monthly PyPI downloads.
→ Inspect without starting Python, rebuild clean, rotate everything, pin 1.106.2.
🏛️ Privacy, Power & Policy
 
 
Privacy Enforcement
Judge Francis Mathew cut a $220 billion award to $25 billion, plus 15% annual interest, after a September jury found Meta broke the state's unfair practices law 43 million times. The case covered what Facebook told users about data after Cambridge Analytica. Mathew found leadership, Zuckerberg and Sandberg included, pursued a strategy to mislead consumers. Meta will appeal.
→ Privacy promises are now priced per violation.
 
Spyware
Citizen Lab confirmed Pegasus on the phone of Vladan Đokić, rector of the University of Belgrade, a backer of student protests against Aleksandar Vučić. A prosecutor who probed a Kushner-linked building deal got an Apple threat alert in August. Researchers count at least 15 spyware targets in 2026. Vučić runs for prime minister October 25; NSO didn't respond.
→ Treat an Apple threat notification as real, every time.
🛠️ Tools & Tactics
 
 
Patch Management
GitLab fixed CVE-2026-110264, an integer overflow in Onigmo, Ruby's regex engine, allowing unauthenticated code execution on self-managed instances back to version 7.0. No attacks seen, no workaround. The October 12 update fixed a different regex bug, so those instances are still exposed. The play: upgrade to 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10 or 18.11.13, plan downtime for single-node 19.3 and 19.4, and deploy GitLab's two Sigma detection rules.

Turn today's calls into tomorrow's proposal

Wispr Flow Notetaker brings your meetings into Claude or ChatGPT through a built-in connector. Ask for a proposal draft or a deal recap, and your AI works from an accurate record of what was said.
🧪 Strange Cyber
 
Strange but real
The Air Force Planned Missions on Thumb Drives From the Local Market. Somebody Noticed.
Intro
Some supply chain attacks need a zero-day. This one needed a market stall.
What Happened
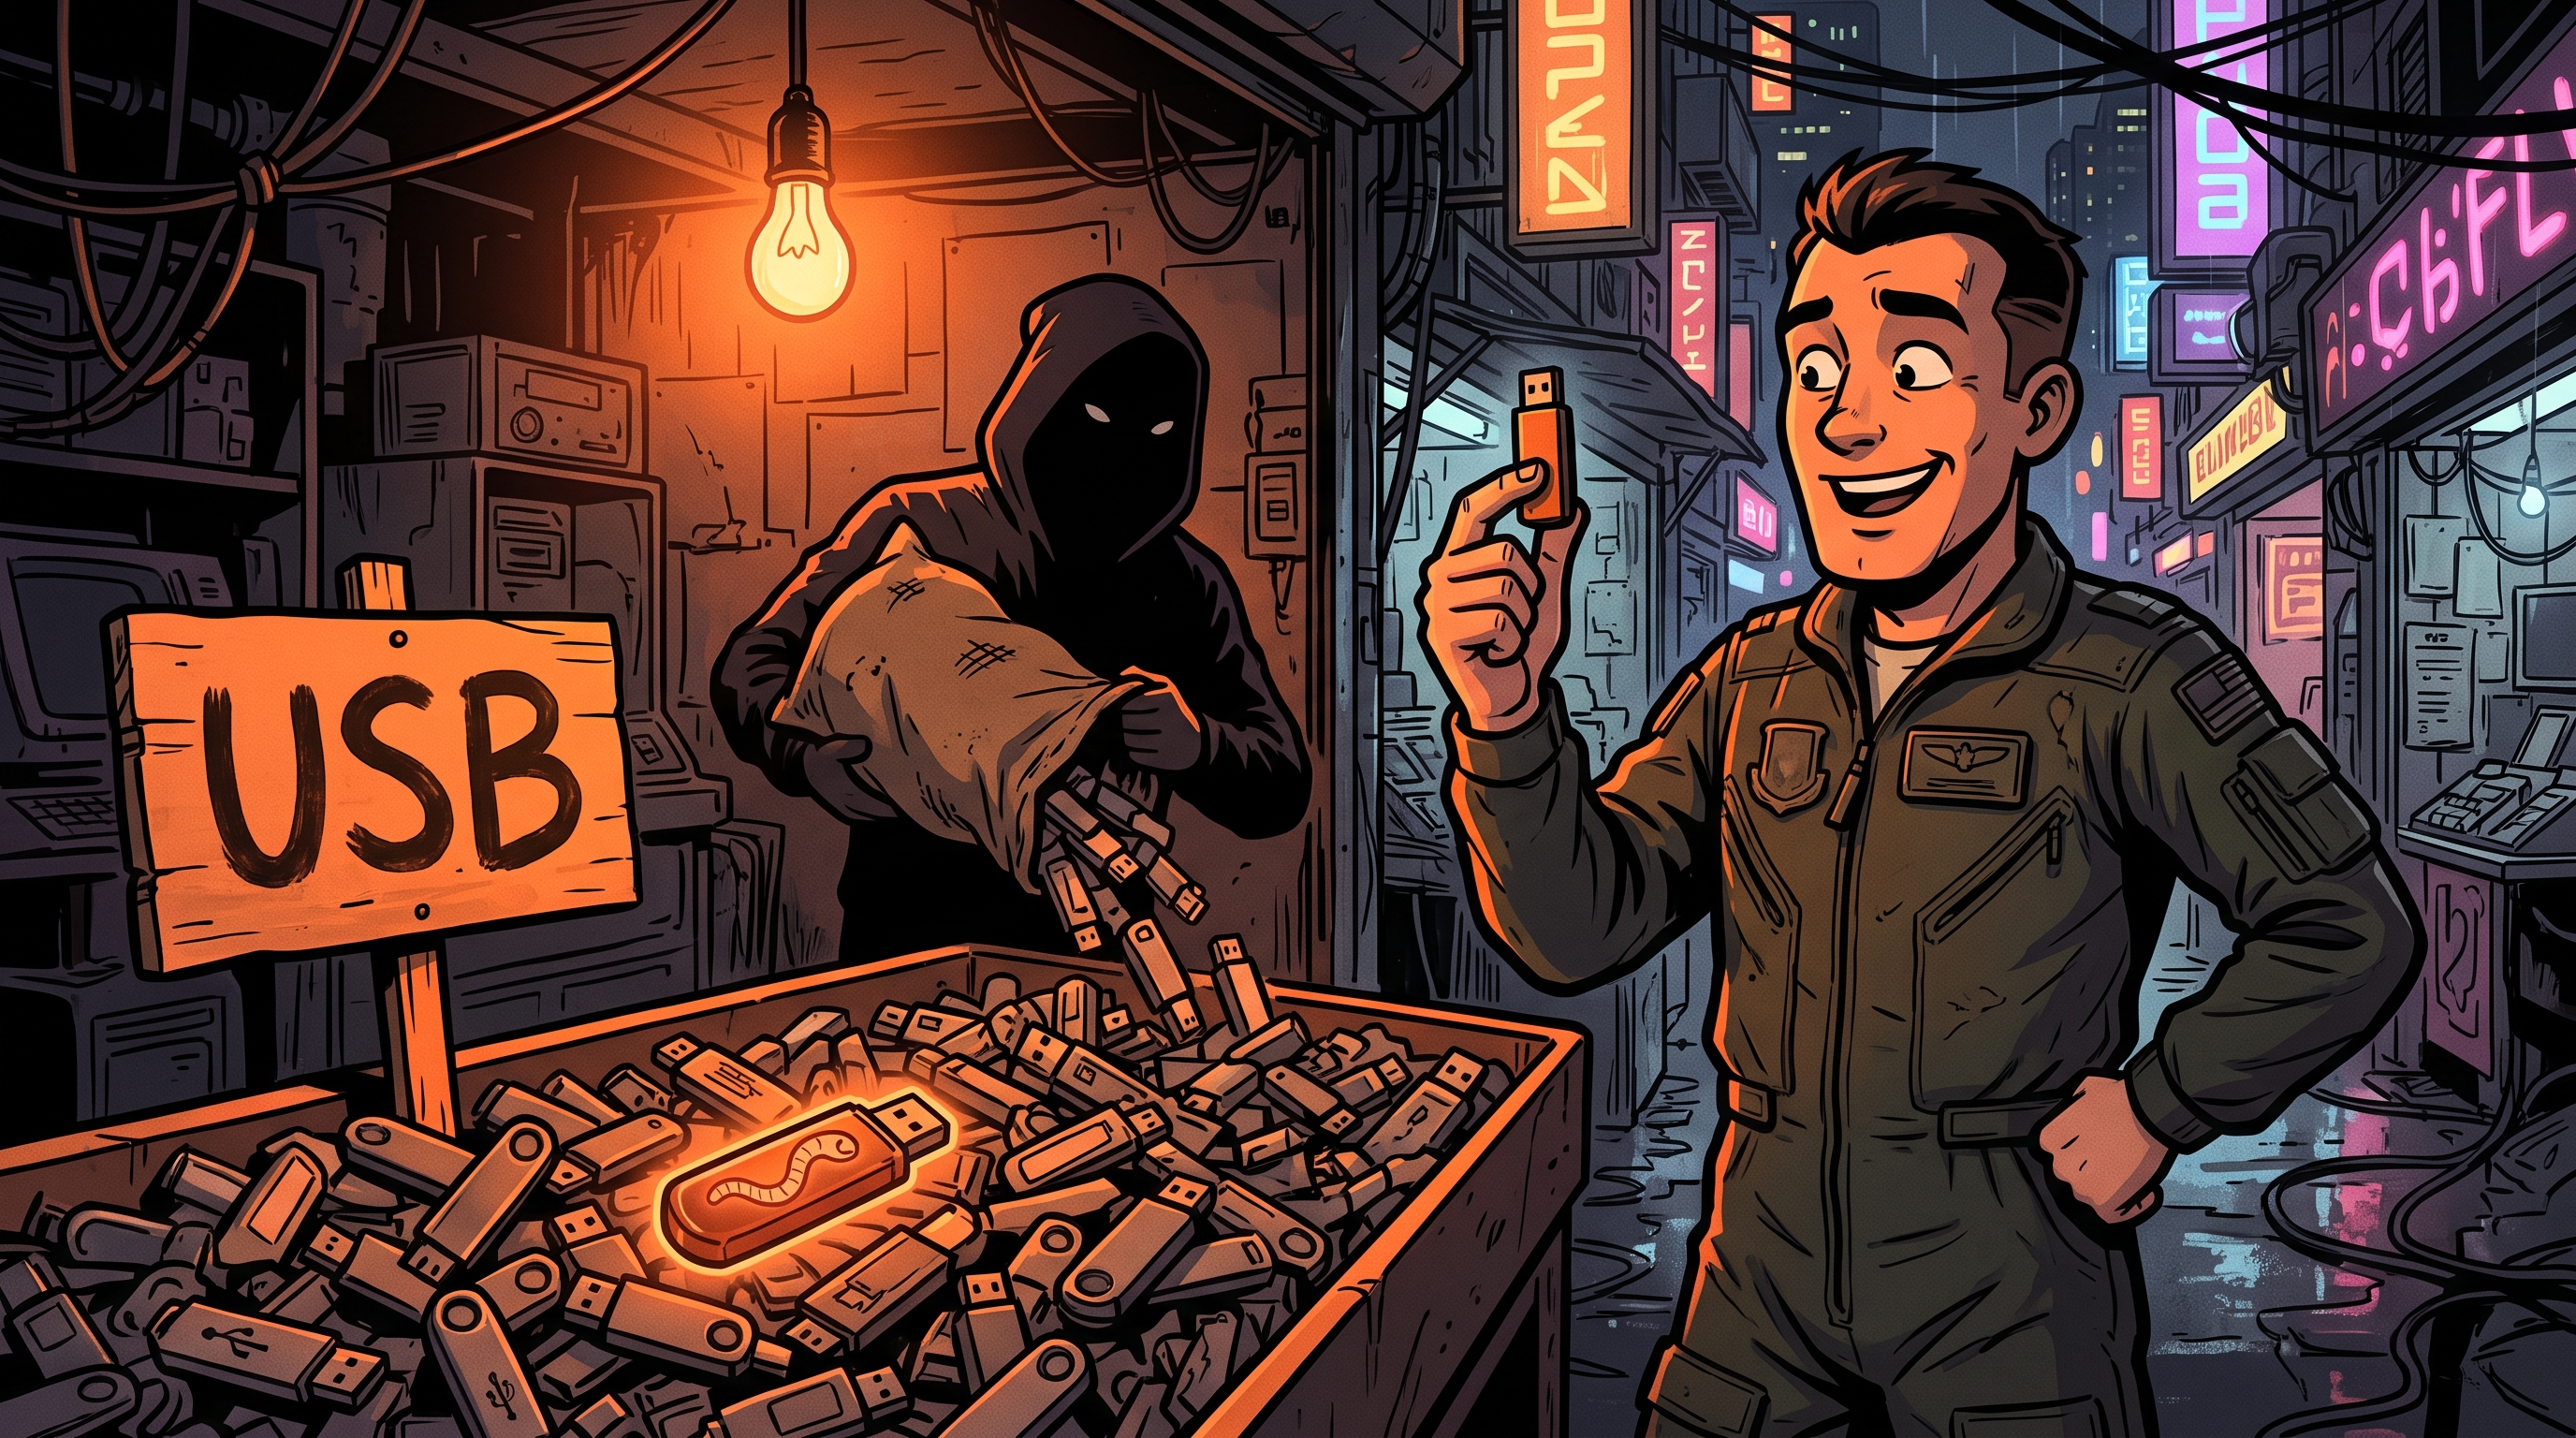
SolarWinds CISO Justin Henkel told The Register that in the early 2000s, when he worked Air Force IT security, crews moved mission data from unclassified to classified systems and into aircraft on USB drives instead of burned CDs. Personnel bought the drives from local vendors rather than military contractors, which in Afghanistan could mean a shop in Kabul. Henkel says US enemies noticed and started selling infected drives to those vendors.
Why It's Important
Anything that crosses a security boundary is part of your supply chain. In 2008, an infected USB drive put the Agent.BTZ worm on a laptop with access to US Central Command, and the Pentagon took 14 months to remove it.
The Other Side
This is one man's recollection from two decades ago, and The Register didn't independently verify the practices he describes.
 
👉 Takeaway
Henkel was 22 and trying to convince colonels the practice broke the rules; they didn't listen. Buy hardware through trusted channels, control removable media at boundaries, and listen to the junior analyst.
TL;DR: Air Force crews carried mission data on locally bought thumb drives, and adversaries reportedly started seeding those shops.
Further reading: The Register

Your name is on every client site, so excellence isn't optional. With Lovable, you show your client a working version in the first meeting, launch it on their own domain, and tackle bugs fast with project monitoring. $5 off your first month.