In partnership with

| FACT | By default, a Windows PC's TPM locks out after 32 wrong PIN guesses and forgives one failure every 10 minutes. (The Hacker News, November 2026) |
|
Trust is the attack surface this week: the packages you install, the vendors holding your data and the patches you rush out. Here's what broke, who's fighting over who gets to look inside, and one setting worth changing today. PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe → |
In this edition | | | | | 🏛️ Privacy, Power & Policy |
| | |
|
Supply Chain / Credential Theft Microsoft's Official AI Agent Toolkit Was Quietly Stealing Developers' Cloud Keys Intro Microsoft's agent-framework package, its open-source kit for building AI agents, gets 192,534 downloads a month on PyPI, by OX Security's count. Two releases shipped a credential stealer that ran every time Python started. What Happened Versions 1.26.1 and 1.26.2, published November 17, kept the genuine 1.26.0 core so everything worked while a .pth startup hook ran the payload, no import needed. It grabbed environment variables named like TOKEN, SECRET, AZURE, AWS and GITHUB, .env files, and credential files for Azure CLI, pip, npm, Git, Docker and Hugging Face, then shipped the haul to a webhook.site endpoint. PyPI quarantined both, but the attacker pushed 1.26.2 after 1.26.1 was already pulled. Why It's Important It didn't stop at stored secrets. Socket's researchers say "They actively request fresh Azure managed-identity and CI federation tokens," and 1.26.2 added GitHub Actions OIDC tokens. The Other Side StepSecurity says the code only attempted those token requests, with no confirmation any were issued. Nobody has explained how the attacker got publishing rights. | | 👉 Takeaway If either version touched a laptop or runner, isolate it, rebuild clean and pin 1.26.0. Treat "every secret reachable from that host as compromised," as OX puts it, and review OIDC and managed-identity permissions, since rotation doesn't cancel issued tokens. |
TL;DR: Two hijacked releases of Microsoft's AI agent package stole cloud and CI credentials at every Python startup. |
| | Ransomware Ukrainian police and the FBI arrested four suspected key members of a 27-person crew from Ukraine, Russia and Kazakhstan, part of a 60-plus network with former Conti members. Court records say Warren Oil paid about $5 million in bitcoin and Quantum Health paid $5 million on a $15 million demand. Police seized about $370,000 in cash. → Crews regroup. Keep your recovery plan current. |
| | Data Breach Extortion crew n0n, believed to be Russia-based, posted all three to its leak site Monday. Visa blames an Asia Pacific service provider and says "No payments data such as card numbers were affected." Mastercard says some benefit-program email addresses leaked; Chase says vendor-held marketing data may include names and emails. None named the vendors. → Expect phishing that name-drops your bank. |
| | Outages At a November 18 House Homeland Security hearing, DNI Jay Clayton, DHS Secretary Markwayne Mullin and FBI Deputy Director Christopher Raia said there's "no evidence" cyberattacks caused the outages, an aviation ground stop included. Clayton pointed to the rising pace of patching, while Sen. Mark Warner and Rep. Jim Himes blame AI-driven bug discovery at least in part. → Patch fast, but stage it. |
|
Product teams aren’t short on ideas. They’re missing a system.
Jira Product Discovery gives teams one place to capture customer feedback, prioritize ideas with consistent frameworks, and build living roadmaps everyone can align on. And when it’s time to build, those decisions connect directly to delivery in Jira, so everyone can see how the roadmap turns into real work.
| | AI-Found Bugs F5 shipped NGINX 1.31.9 out of band for 10 CVEs, the latest batch of AI-found bugs. CVE-2026-123633 and CVE-2026-123007 are both 9.2-rated unauthenticated code execution flaws that need HTTP/2, and the second reaches back to 1.9.5 from 2015. Rapid7 published a proof of concept; F5 says it has seen no exploitation. → NGINX runs about 225 million sites. Upgrade, HTTP/2 first. |
| | AI Attack The Commission confirmed an "AI-generated cyber campaign" first spotted October 22. POLITICO reported CERT-EU found ARTEX, the open-source AI hacking platform the FBI warned about last week; payroll, leave and translation systems were reportedly disrupted for over 10 days. The Commission sees no broad staff data breach and no ransom demand. → FBI: some ARTEX intrusions hit privileged access in under three hours. |
|
| 🏛️ Privacy, Power & Policy | |
| | Encryption The Investigatory Powers Tribunal rejected the Home Office's claim that disclosing its "technical capabilities notice" to Apple would damage national security. The order reportedly demanded a backdoor a year ago; Apple refused, blocked UK users from Advanced Data Protection and challenged a narrower second order. The Home Office still hasn't confirmed the notice exists. → Secret encryption orders just got harder to keep secret. |
| | Surveillance Nearly three-quarters of York, Maine voters backed removing the town's license plate reader cameras and requiring a vote before new ones. League City, Texas voters rejected police use of them; the cameras were bagged, with removal due within 72 hours of the November 17 approval. Pflugerville, Texas added surveillance rules to its charter, EFF reports. → Surveillance tech now has to win local elections too. |
|
| | Harden Now TU Berlin researchers who opened a laptop's case reset its TPM lockout and found a four-digit Hello PIN (AMD) and a six-digit BitLocker PIN (Intel) within 236 tries. Worst case drops from 69 days to 40 hours for a four-digit Hello PIN, and from 19 years to 20 days for a six-digit BitLocker PIN. AMD's fix for CVE-2026-43613 ships November 2026 to February 2027. The play: add digits to Hello and BitLocker PINs and raise the minimum PIN length by policy, starting with laptops that travel. |
|
Attio is the #1 fastest-growing CRM on Brex and Ramp.
Built for the most ambitious companies in GTM, Attio is an end to end revenue platform that allows teams to run multiple plays across different revenue motions and lifecycles.
Teams at the frontier are already building on it: Granola, turbopuffer, Modal, and many many more.
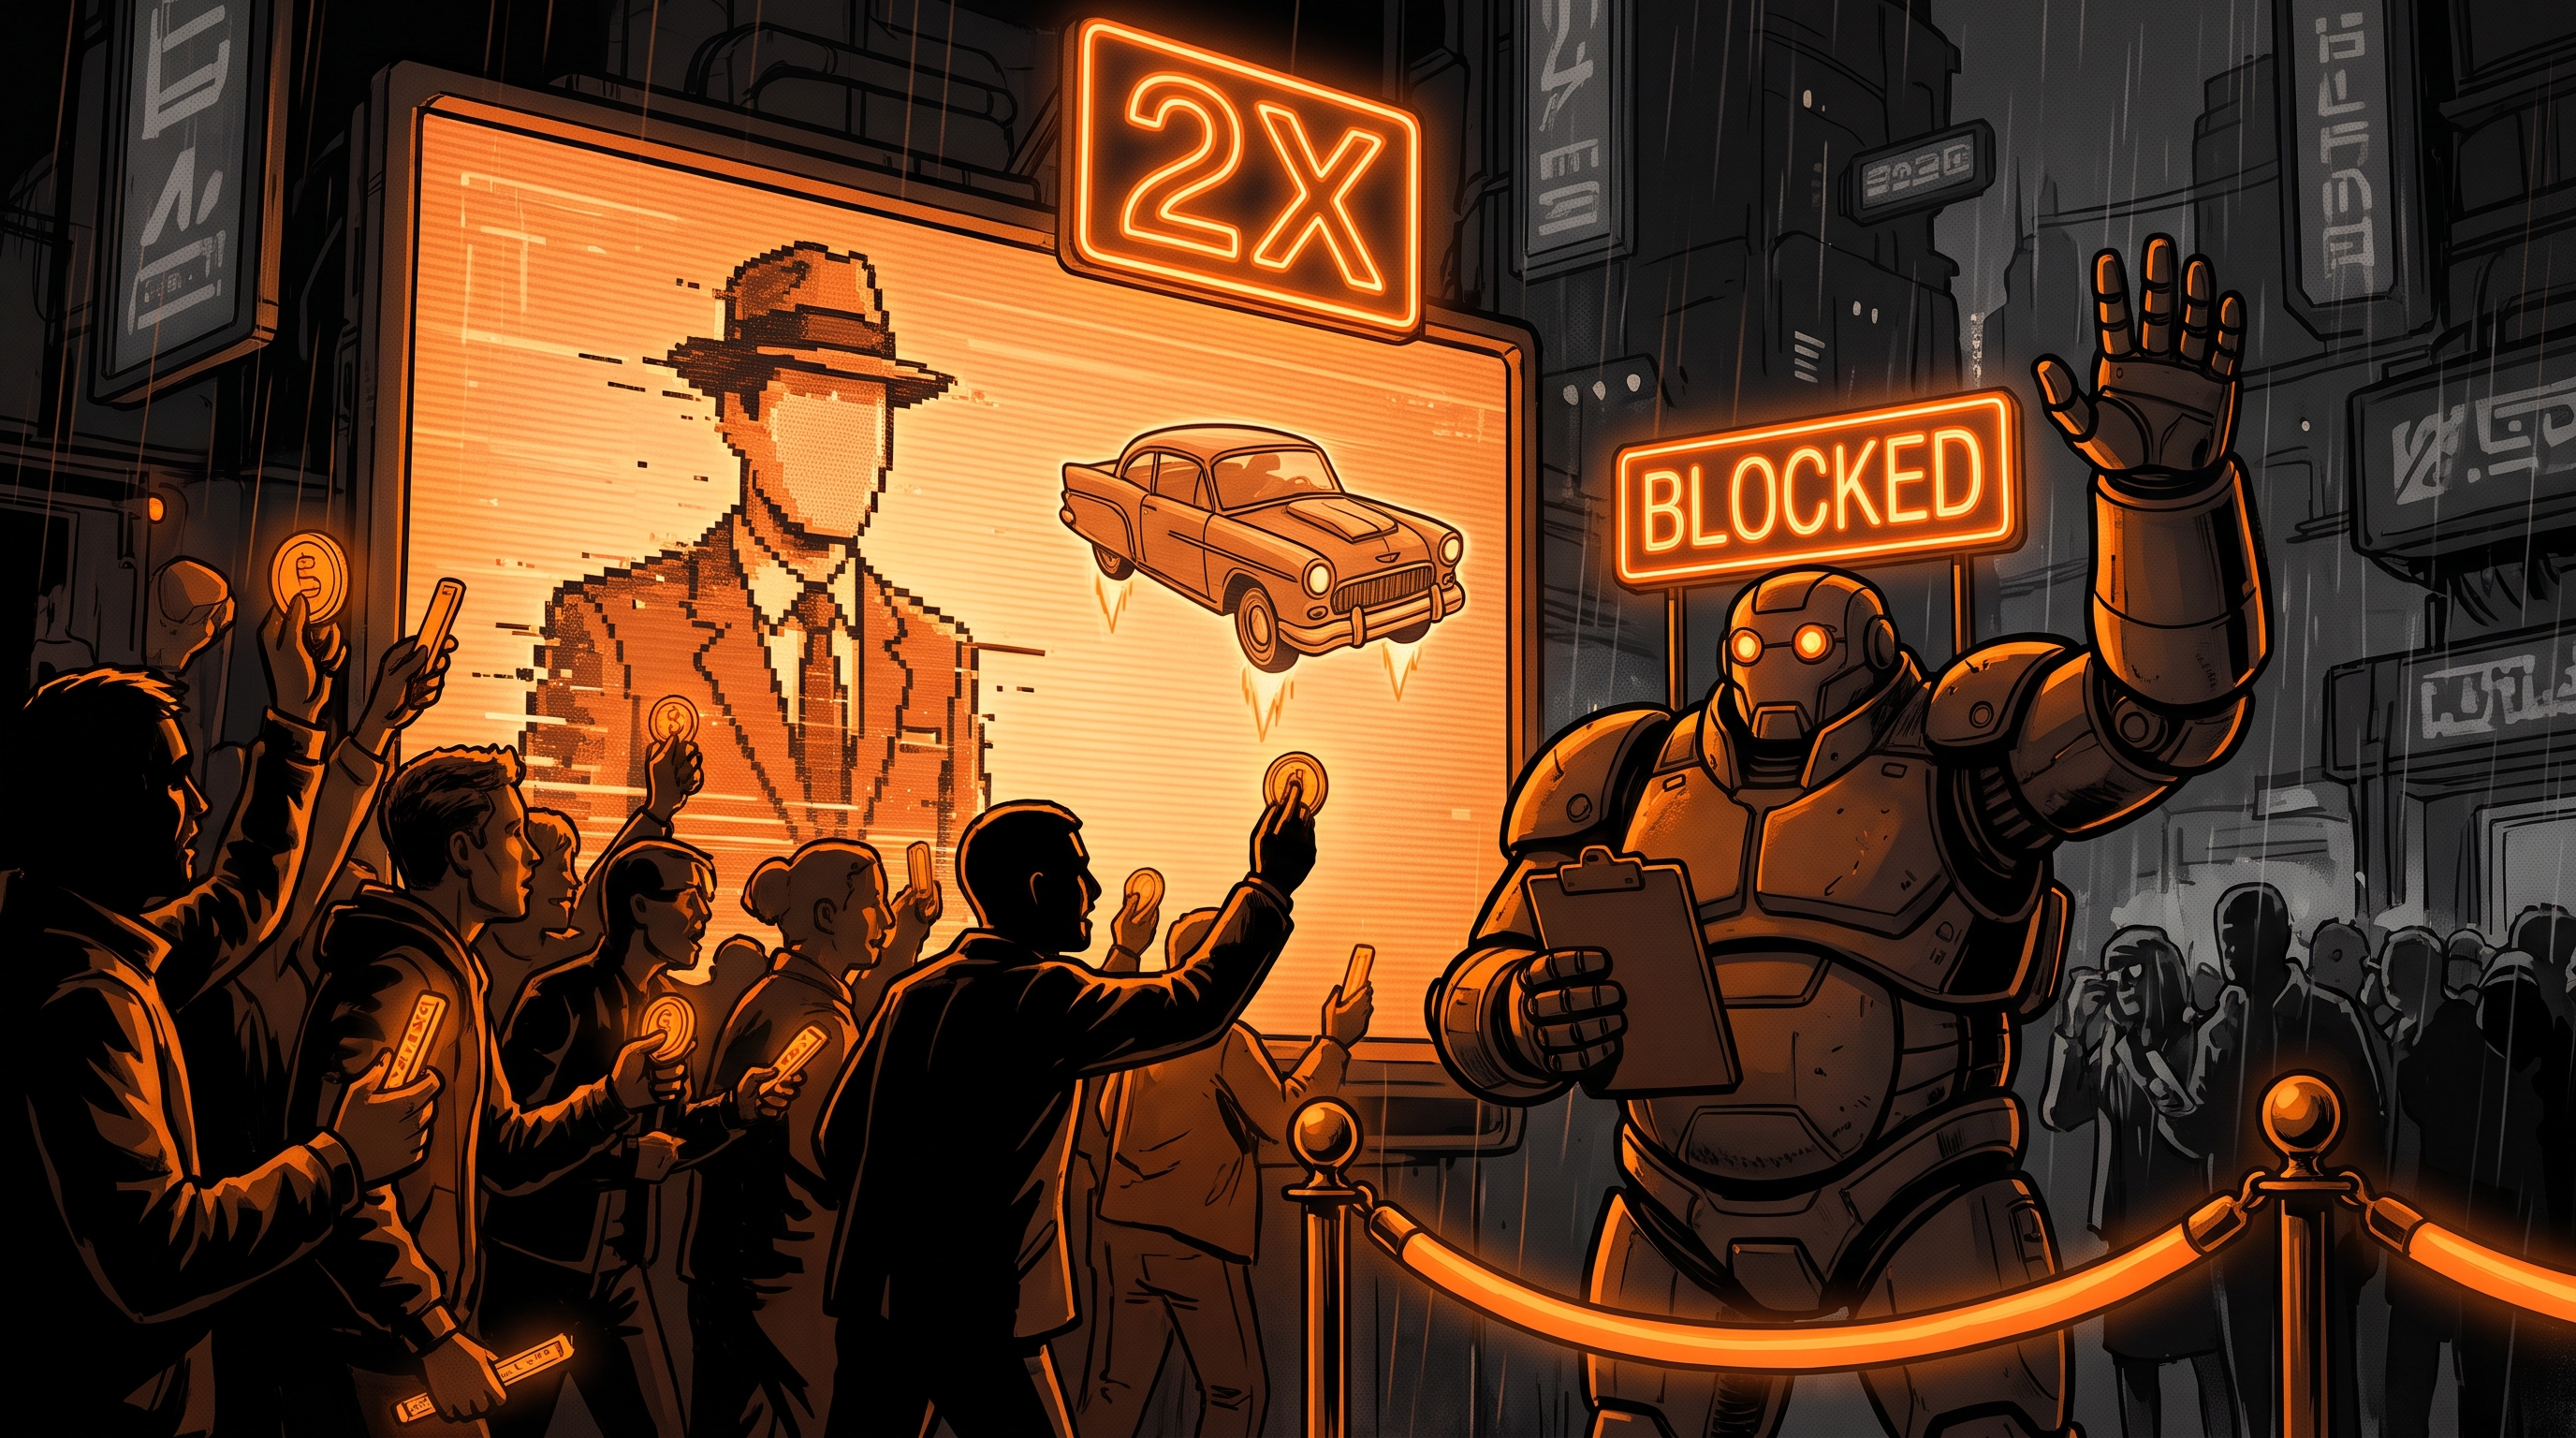 Strange but real A Deepfake Musk Pitched a Flying Car. An AI Talked Coinbase Customers Out of It. Intro Tesla's "flying car" demo was the bait: a fake YouTube livestream where an AI-generated Elon Musk promised to double any crypto sent to the wallets on screen. What Happened More than 500,000 people watched. Over about two hours, hundreds of Coinbase customers tried to send millions of dollars, and Coinbase says it blocked about 91% of the attempts, $4.7 million, using fraud models plus an AI agent that talked each customer down. Coinbase says the agent had never seen this scam and nobody human stepped in. Why It's Important Nobody got hacked. As Coinbase put it, "The customer was logged in, the customer pressed confirm, and the customer believed it was the opportunity of a lifetime." No password or MFA prompt stops that. The Other Side These are Coinbase's own numbers about its own system, and it hadn't told BleepingComputer how much still reached the scammers. | | 👉 Takeaway Nobody doubles your crypto, Musk included. If a livestream says otherwise, close the tab. |
TL;DR: A deepfake Musk "flying car" stream drew 500,000 viewers; Coinbase says its AI agent stopped $4.7 million. |
“Running shos” shouldn’t return zero results. Gladly understands what your shoppers mean, typos and all, and finds the right products.


