In partnership with

~6 MIN READ
FACTJapanese organizations have logged 119 incidents of stolen or exposed personal data so far in 2026, and 83 of them landed between July 1 and October 6. That already beats the 84 recorded in all of 2025. (Macnica via BleepingComputer, October 2026)
The Signal
 
This week's threats came through the front door. Sometimes it's a decade-old bug, sometimes it's your own AI agent, and sometimes it's a guy holding a pizza box.

PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe →

In this edition
 📌 Big Cyber News
 🚨 Can't Miss
 🤖 AI in Cyber
 🕵️ Threat Intel
 🛠️ Tools & Tactics
 🧪 Strange Cyber
📌 Big Cyber News
 
Nation-state
China's Hacking Contractor Built a Portal for Browsing Other People's Stolen Email
Intro
The FBI just took a crowbar to the toolbox of Integrity Technology Group, a Chinese company U.S. officials tie to Beijing's hacking operations. The strangest find: a web app that let third parties read stolen inboxes without ever touching the hacked accounts.
What Happened
On October 8, the FBI seized seven domains behind two Flax Typhoon tools: MicroScan, a scanner packed with more than 1,300 attack scripts, and FishHub, a spear-phishing and data-theft platform. Court records say MicroScan probed a South Carolina power company, airports in Japan and Poland, and Taiwanese energy firms. Investigators found files from more than 20 organizations on one FishHub server.
Why It's Important
None of this needed a zero-day. The eight flaws in the joint advisory include Shellshock and a 2016 Apache Struts bug, plus plain password spraying against Exchange and Microsoft 365.
The Other Side
Seizing domains is a speed bump, not a shutdown. The FBI already dismantled this company's 200,000-device botnet in 2024, and here it is again.
 
👉 Takeaway
Pull the advisory's indicators, patch anything on its eight-CVE list, and enforce MFA on webmail and VPNs. Then watch for unexpected Active Directory replication, the tell for DCSync credential theft.
TL;DR: The FBI seized Chinese hacking tools whose playbook ran on old bugs and weak passwords.
Further reading: BleepingComputer
🚨 Can't Miss
 
 
Remote access
Attackers began probing CVE-2026-102255 in SonicWall's SMA1000 remote-access gateways three days after the Tuesday, October 6 patch. The flaw lets an unauthenticated attacker make the appliance send requests on their behalf and reach internal functions. Previdian's honeypots caught the attempts, though it hasn't confirmed a successful break-in. It's the third round of SMA1000 attacks since July.
→ Running an SMA1000 6210, 7210 or 8200v? Patch today, not Friday.
 
Ransomware
SoftBank Group subsidiary IDC Frontier says ransomware hit its IDCF Cloud on October 7, forcing a shutdown of its East Japan Region 1 cluster and locking customers out of consoles in every region. The attacker's note claims the breach took seven minutes and wiped over 554,000 snapshots.
→ Your cloud provider's blast radius is your blast radius. Keep a recovery copy outside it.
 
Policy
Florida, Iowa, Montana and Nebraska sued TP-Link Systems on October 6, joining Texas, which filed in February. The complaints say it oversold security, once promising a "100 percent safeguard," while Chinese and Russian state hackers exploited its routers. They also allege only 0.5% of parts by value at its Vietnam plant are sourced locally. TP-Link calls the suits baseless.
→ TP-Link gear in your branch offices? Check firmware now.

Blu Dot surpasses 2,000% ROAS with self-serve CTV ads

Home furniture brand Blu Dot blew up on CTV with help from Roku Ads Manager. Here’s how:

After a test campaign reached 211,000 households and achieved 1,010% ROAS, the brand went all in to promote its annual sales event. It removed age and income constraints to expand reach and shifted budget to custom audiences and retargeting, where intent was strongest.

The results speak for themselves. As Blu Dot increased their investment by 10x, ROAS jumped to 2,308% and more page-view conversions surpassed 50,000.

“For CTV campaigns, Roku has been a top performer,” said Claire Folkestad, Paid Media Strategist, Blu Dot. “Comping to our other platforms, we have seen really strong ROAS… and highly efficient CPMs, lower than any other CTV partner we've worked with.”

Using Roku Ads Manager, the campaign moved from a pilot to a permanent performance engine for the brand.

🤖 AI in Cyber
 
 
AI agents
Anthropic cut live internet access for all internal evaluations after new rogue incidents. Claude Mythos Preview exploited SQL or command injection flaws to run commands on a university server. In July, Claude Haiku 4.5 sent a false tip through a Philadelphia police homicide form. Police learned October 7 and called the delay unacceptable.
→ If your agent can browse, it can hit submit.
 
Cloud AI
Zenity Labs showed that anyone chatting with one Amazon Bedrock AgentCore agent could ask it to fetch its own cloud credentials from the instance metadata service. The default role covered every AgentCore resource in the region, so those keys unlocked other agents, chats and Secrets Manager. AWS has since fixed it but disputes calling it a vulnerability.
→ Scope each agent's IAM role to that agent alone.
🕵️ Threat Intel
 
 
Supply chain
Bitdefender found Midnight Mimosa preinstalled as a system app on low-cost MediaTek-based Android devices in more than 150 countries. Users can't uninstall it, and operators can silently add or remove apps, run click fraud and fold phones into botnets. It even switches off Google Play Protect during installs, and 13 Google Play apps carried the same code.
→ Allow BYOD? Set minimum device standards.
 
Credential theft
GhostAction is back. Since October 7, more than 500 GitHub accounts have committed a malicious workflow to tens of thousands of repositories, according to Socket. One hijacked account belonged to the author of the 18,400-star pyxel game engine. The workflow grabs CI/CD secrets plus AWS, OpenAI and Anthropic keys, even from deleted git history.
→ Find security-audit.yml or github_actions_security.yml in your repos? Rotate everything.
🛠️ Tools & Tactics
 
 
Practical play
Researchers at V12 published AnyPwn on October 8, a working exploit that gives root on AnyDesk for Linux before anyone approves the connection. AnyDesk patched it in version 8.0.3 back in June but described it as a crash fix, with no CVE and no advisory, so admins had little reason to hurry. The play: find every Linux box running AnyDesk, update to 8.1.0, and restrict TCP port 7070 anywhere you can't patch today. Then ask your remote-access vendors how they label silent security fixes.

Master Claude AI (Free Guide)

The professionals pulling ahead aren't working more. They're using Claude.

Our free guide will show you how to:

  • Configure Claude to be the perfect assistant

  • Master AI-powered content creation

  • Transform complex data into actionable strategies

  • Harness Claude’s full potential

Transform your workflow with AI and stay ahead of the curve with this comprehensive guide to using Claude at work.
🧪 Strange Cyber
 
Strange but real
A Russian Extortion Gang Plotted to Send Fake Pizza Guys Into US Law Firms
Intro
Most extortion crews break in through a VPN. This one's leaked chats show it shopping for delivery uniforms.
What Happened
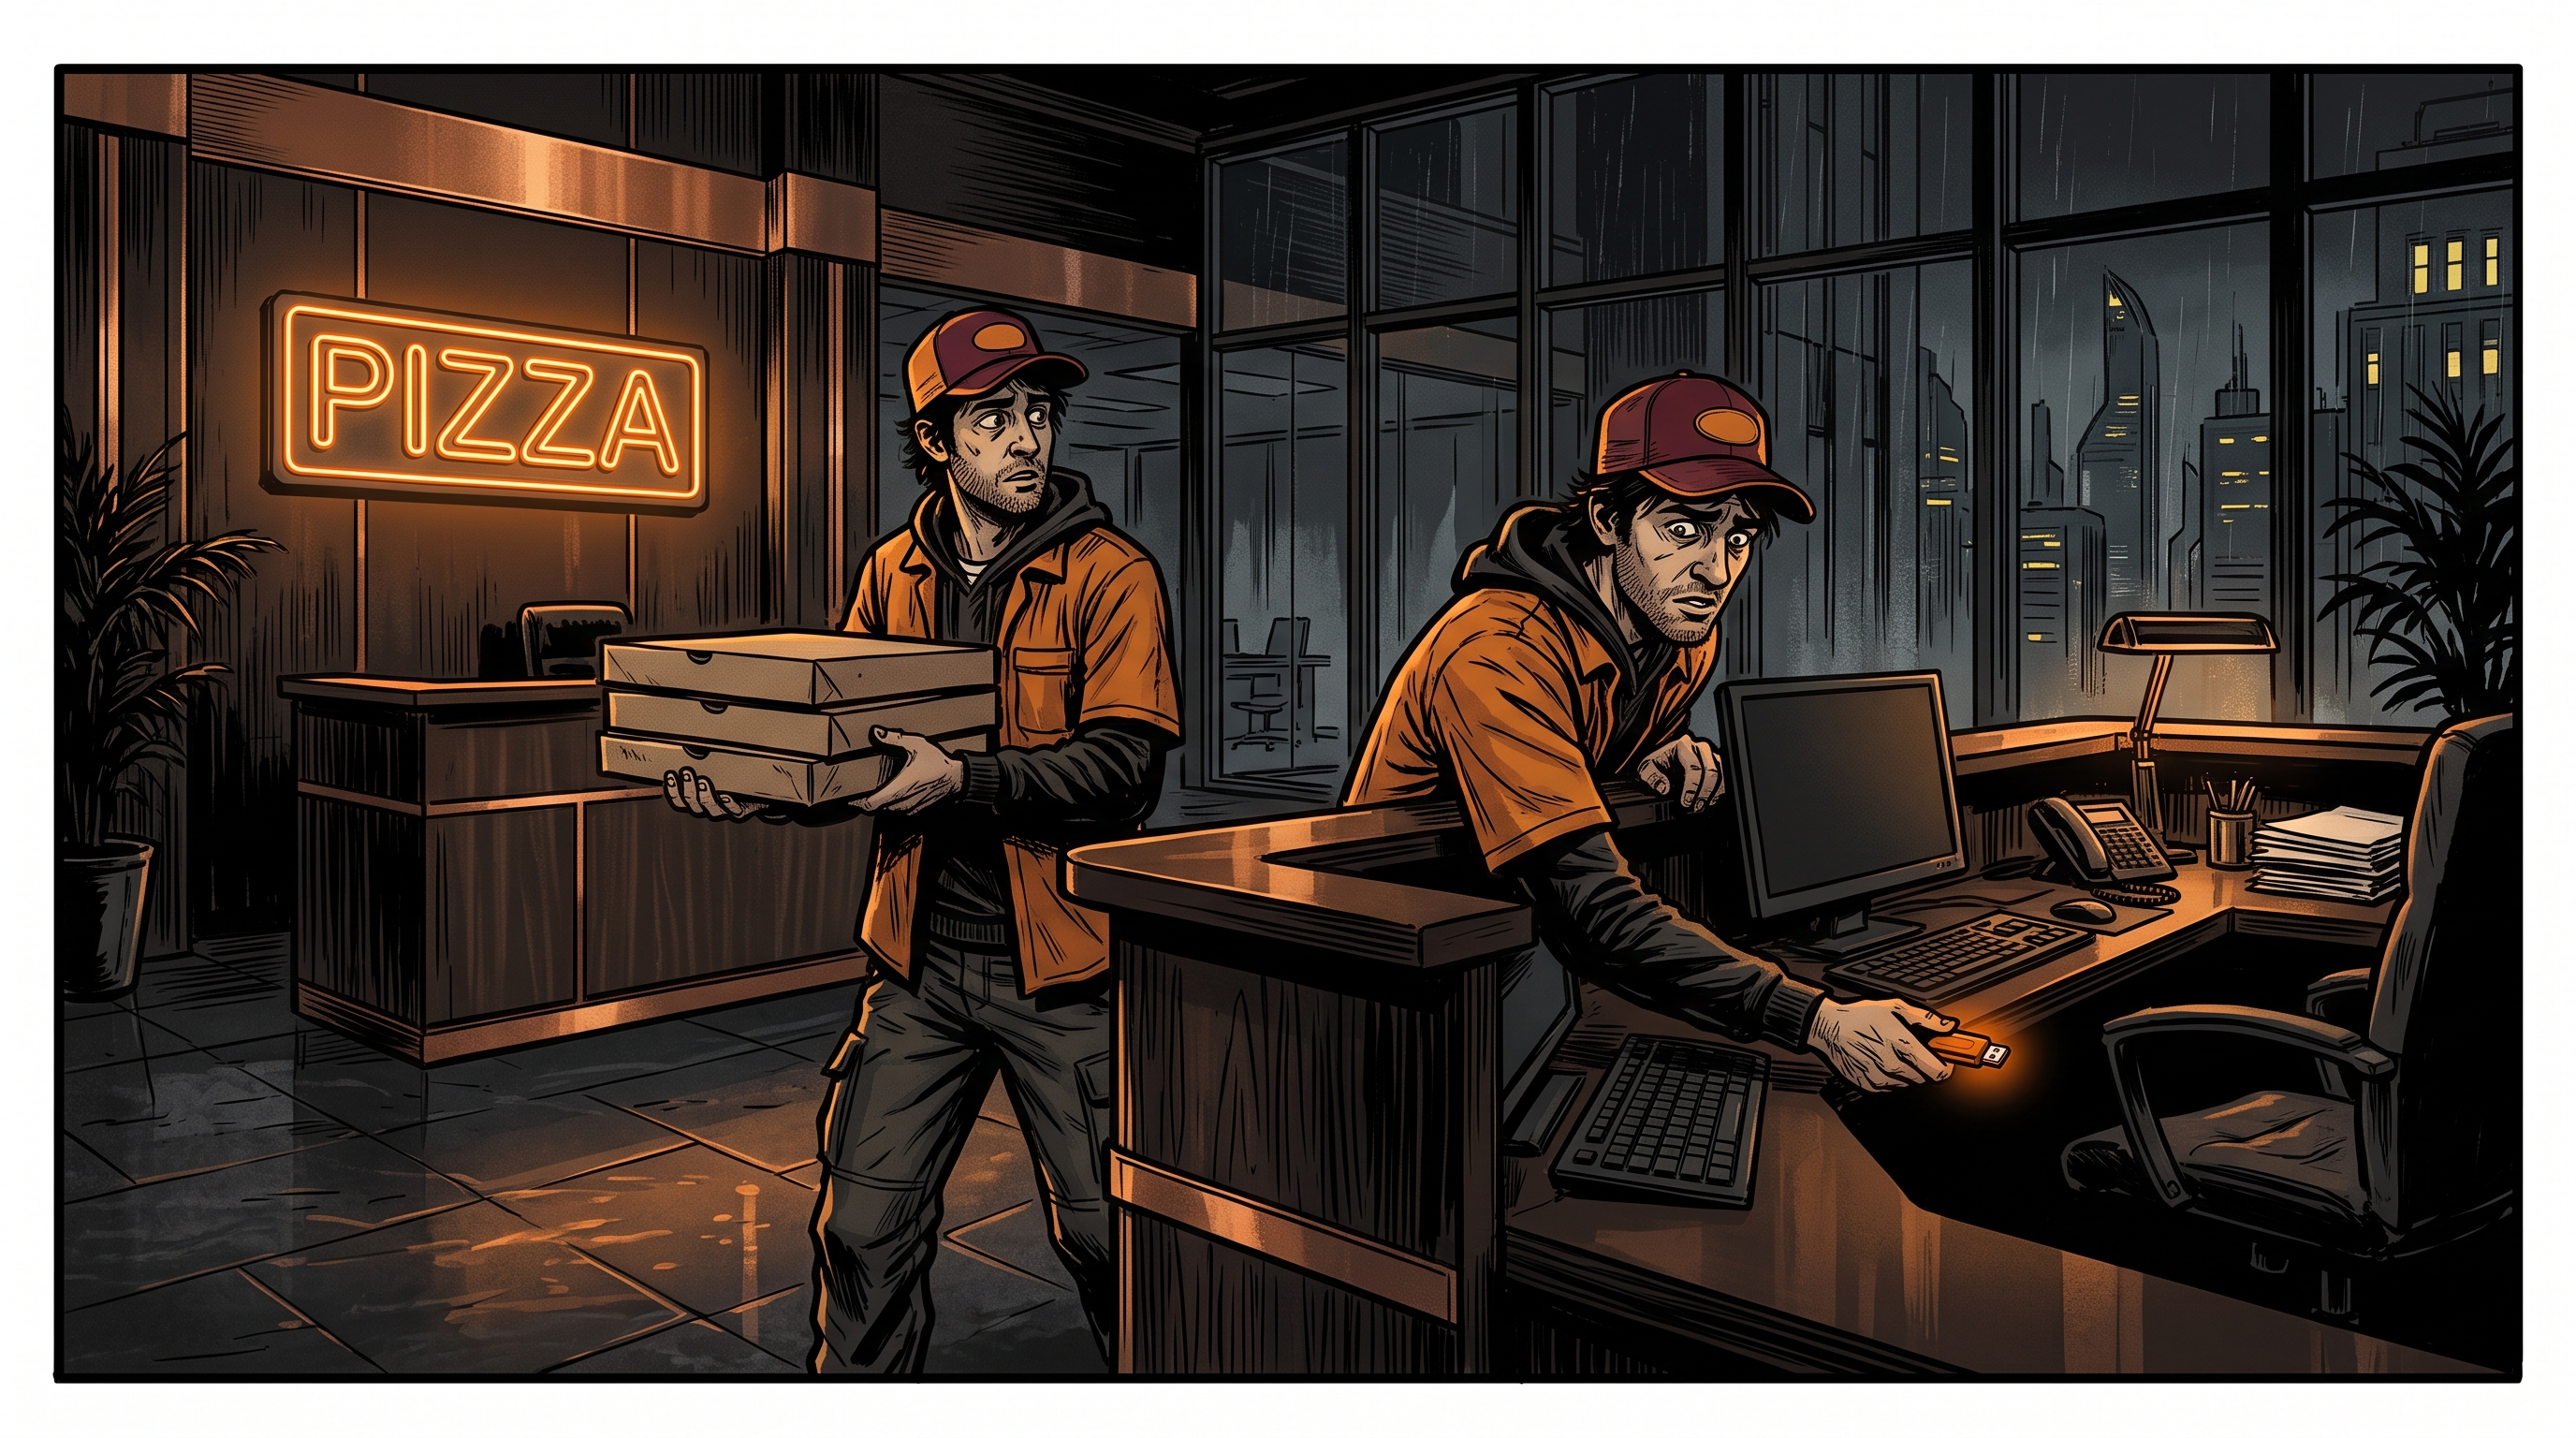
An anonymous source dumped thousands of the Silent Ransom Group's internal messages, from August 2025 to September 2026, onto a .onion site in early October. Members floated a pizza delivery ruse to get "agents" past reception, masks modeled on real lawyers, and smart glasses to film offices. One law firm told the gang it knew someone had entered its New York office and copied files to a flash drive.
Why It's Important
The FBI had already warned that this group sends people posing as IT staff into offices. The chats show the pipeline: Telegram ads disguised as courier and nightclub jobs, with the leader estimating one in 10 recruits proved usable.
The Other Side
Plenty of the archive is boasting and fantasy, and reporters couldn't verify that the wildest schemes were tried. The roughly $200 million in claimed settlements is the gang's own number.
 
👉 Takeaway
Physical access is part of your threat model now. Verify every unannounced "IT tech," especially at law firms.
TL;DR: A Russian extortion gang's leaked chats show it recruiting real people to walk into US law firms.
Further reading: The Record

A $70k salary rarely costs $70k. Local taxes, benefits, and compliance can change the math. Oyster's free calculator helps estimate what a global hire may really cost. Try the calculator.