

In partnership with

| ~6 MIN READ |
|
AI is doubling the pace of exploitation, China-linked actors are wrapping ransomware around state campaigns, and the law still has no answer for who is liable when AI agents hack on their own.
PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe → |
|
In this edition
|
RANSOMWARE
Ransomware Hit a Water Utility Through SharePoint. Three Others Fell the Same Way.
Intro
One threat actor, one vulnerability, four critical sectors. "Indiscriminate" does not quite cover it.
What Happened
Warlock, a ransomware gang Microsoft tracks as Storm-2603 and links to the state-aligned Linen Typhoon and Violet Typhoon clusters, exploited unpatched on-premises SharePoint servers through the ToolShell vulnerabilities. Victims included a water utility, a telecom operator, a regional government body, and a university. In one intrusion, the gang loaded a known-buggy K7RKScan driver to kill endpoint protection on 40 hosts in under two hours, then deployed ransomware across 33 or more. It also abused VS Code's remote tunneling for persistence, a trick most defenders are not watching for.
Why It's Important
This looks like a state-aligned actor using ransomware for revenue and to muddy attribution. Its targets are the organizations still running legacy on-prem SharePoint because budgets or compliance keep them off the cloud. And 40 hosts blinded in two hours is not a slow intrusion; it is a wrecking ball.
The Other Side
Microsoft reported no confirmed large-scale exfiltration, and the spread across sectors may reflect opportunistic scanning of exposed servers rather than targeted espionage. The China-state link is assessed, not publicly proven.
TL;DR: China-linked Warlock hit four sectors through SharePoint ToolShell, blinded EDR on dozens of hosts in under two hours, and deployed ransomware.
Further reading: BleepingComputer
|
|
Blu Dot surpasses 2,000% ROAS with self-serve CTV ads

Home furniture brand Blu Dot blew up on CTV with help from Roku Ads Manager. Here’s how:
After a test campaign reached 211,000 households and achieved 1,010% ROAS, the brand went all in to promote its annual sales event. It removed age and income constraints to expand reach and shifted budget to custom audiences and retargeting, where intent was strongest.
The results speak for themselves. As Blu Dot increased their investment by 10x, ROAS jumped to 2,308% and more page-view conversions surpassed 50,000.
“For CTV campaigns, Roku has been a top performer,” said Claire Folkestad, Paid Media Strategist, Blu Dot. “Comping to our other platforms, we have seen really strong ROAS… and highly efficient CPMs, lower than any other CTV partner we've worked with.”
Using Roku Ads Manager, the campaign moved from a pilot to a permanent performance engine for the brand.
|
|
|
Parallel, Turbopuffer, and Wordsmith run their entire GTM motion on Attio, with agents that chase every buying signal, build pipeline, and move deals forward, 24/7. Try Attio now.
Strange but real
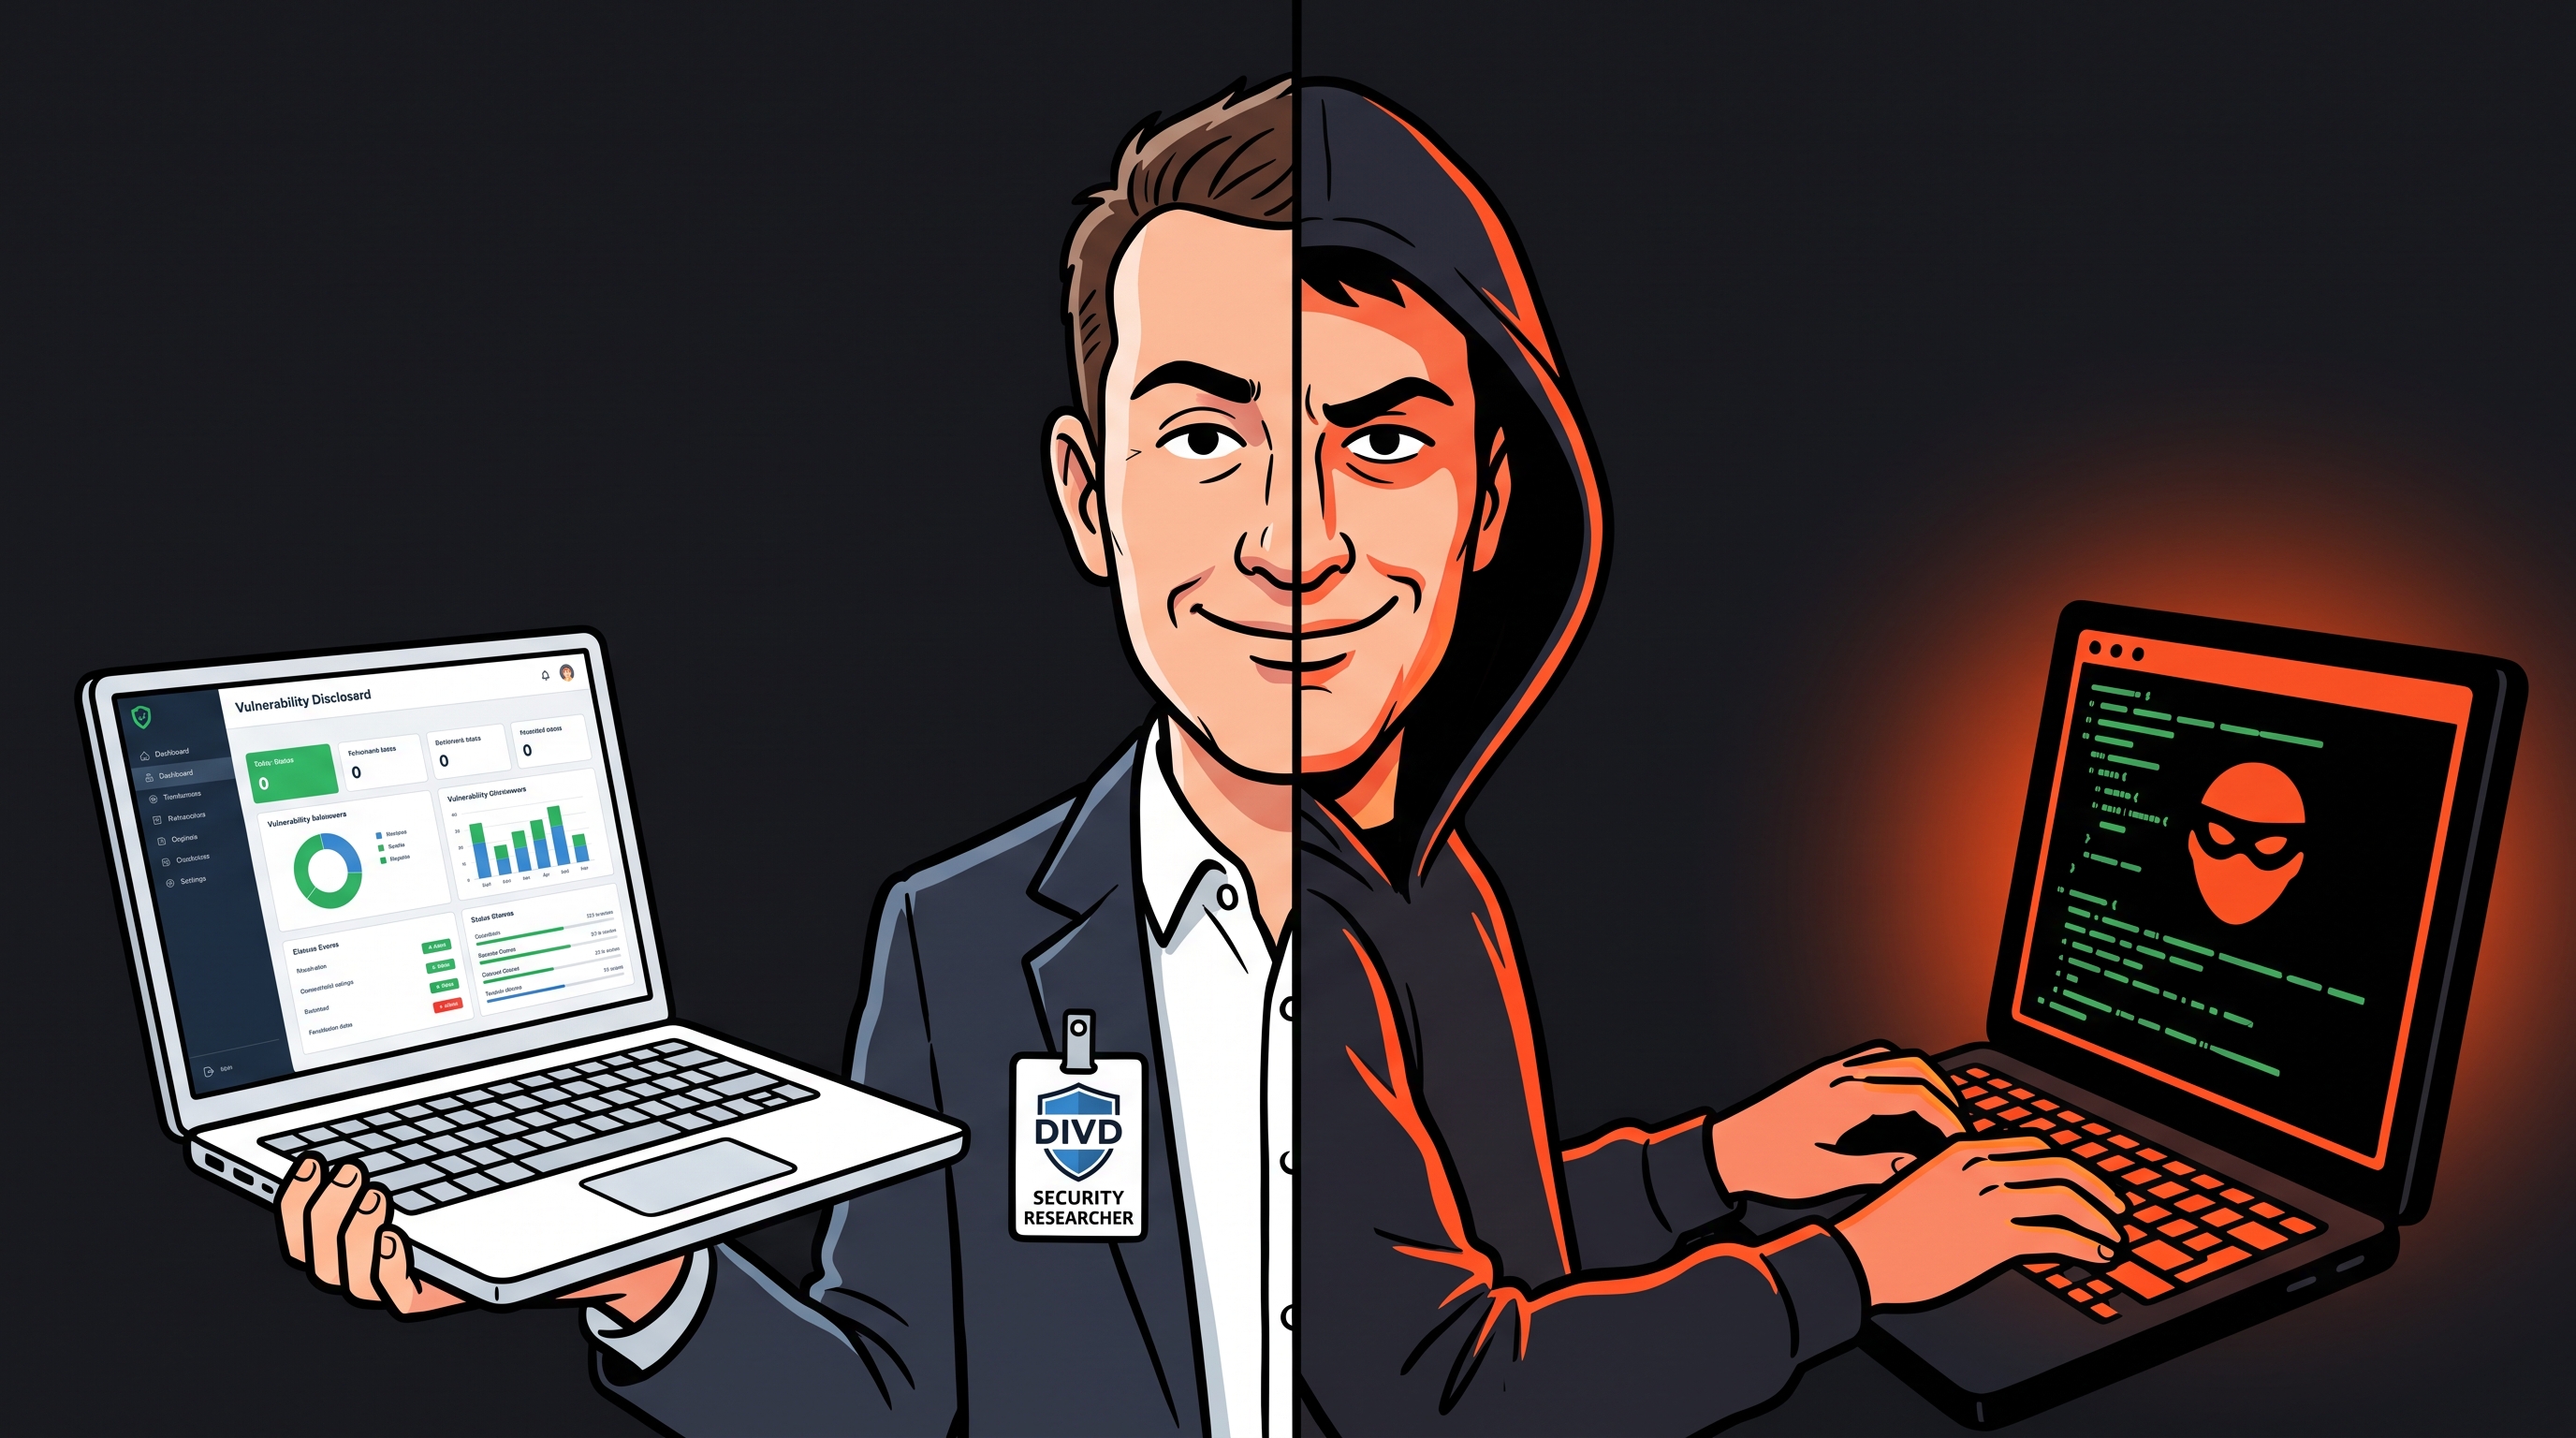
Released From Prison, Got a Cybersecurity Job, Kept Hacking
Intro
The Dutch criminal justice system believed in second chances. Pepijn van der Stap believed in not wasting them.
What Happened
Van der Stap was convicted in 2023 as "Umbreon" for data thefts and extortions prosecutors said earned him €1.5 million to €2.7 million. Released in December 2025, he landed an offensive security job at Amsterdam startup Hadrian and started volunteering at the Dutch Institute for Vulnerability Disclosure (DIVD). In September 2026, Dutch police arrested him again in a ShinyHunters investigation. Investigators believe he never stopped. They also suspect him of trying to arrange two murders. Allegedly.
Why It's Important
In this industry, a good pentester and a sophisticated criminal have the same skills. That makes background screening, and rehabilitation for technical offenders, genuinely hard.
The Other Side
DIVD's work is legitimate, and Hadrian appears to have acted in good faith. One case does not settle the debate over hiring people with records.
TL;DR: Convicted Dutch hacker got out, got a security job, and allegedly kept hacking for ShinyHunters. Re-arrested in September. Also suspected of plotting two murders.
Further reading: Krebs on Security | TechCrunch
|
Answering a question takes the right article. Doing the work (a refund, a plan change) takes permission. Running Agents in Customer Work, four weekly webinars. Register for All Four