In partnership with

| FACT | Claroty's Team82 counted more than 2,700 Danfoss refrigeration controllers exposed to the internet, and showed a compromised one could switch off cooling while still reporting normal temperatures. (Claroty Team82 via The Record, October 2026) |
|
This edition is about the things you'd already checked off: patched appliances, allowlisted sandboxes, locked meeting rooms. Plus AI making serious exploit work a lot cheaper. PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe → |
Zero-Day / VPN Attackers Spent 10 Days Rooting Fully Patched Ivanti VPNs Before the Warning Came Intro "Fully patched" is supposed to end the conversation. On Ivanti Connect Secure this month, it didn't. What Happened While investigating an incident at a customer, Volexity found a previously undocumented group it tracks as UTA0576 chaining three zero-days for unauthenticated root code execution on a fully patched Connect Secure appliance, with exploitation dating to October 3. Ivanti disclosed CVE-2026-104935, which covers the authentication bypass and remote code execution bugs, on October 13 and says "a limited number of customers" were hit. Once in, the attackers stole domain credentials stored on the appliance, searched Active Directory for LAPS passwords and BitLocker recovery keys, sprayed passwords, and tampered with logs. Why It's Important The third bug, a privilege escalation flaw, still has no fix; Ivanti says one is coming "over the coming weeks." Volexity also assesses with medium confidence that the group uses LLMs for exploit development and post-exploitation work. The Other Side Volexity found no backdoor or web shell and disrupted the operation before the attackers' goals were clear. It assesses, with low confidence, that the crew is criminal rather than espionage-focused. | | 👉 Takeaway Update to ICS 22.8R2.5, 25.1.1.2, 25.1.3.0, or 25.1.3.1 now, then treat every credential stored on the appliance as burned and rotate it. Watch for password spraying coming from the VPN. |
TL;DR: A new crew chained three Ivanti zero-days to root patched VPNs, and one bug still has no fix. |
| | Critical Infrastructure In an overnight attack reported Sunday, October 11, someone remotely triggered defrost on refrigeration units at about 300 Intermarché and Netto stores and under 100 Coopérative U stores, spoiling fresh food. BFMTV reports the controllers were made by Danfoss and that older software was targeted; Danfoss has not confirmed. ANSSI is responding; the attacker is unknown. → Refrigeration and HVAC controllers are OT. Find out who can reach yours remotely. |
| | Exploited Vuln Cisco says attackers are exploiting CVE-2026-76519 (CVSS 9.8) in Secure Email Gateway, letting an unauthenticated sender's attachment write files and run commands as root. It applies when File Reputation is enabled and Content Scanner Tools is older than 25.3.0.5525. Fixes: AsyncOS 15.5.5-014 or 16.5.0-780. Release 16.0 has no fix, and there's no workaround. → After patching, run grep "System Security" system_logs on every cluster member. Clean isn't conclusive. |
| | Cybercrime With Japan's National Police Agency and Health-ISAC, Microsoft used a US court order to seize domains behind YAM Store, CoGUI, and Iron Man. Since January they enabled 750 million+ messages impersonating 75,000+ organizations in 150+ countries. Iron Man sold 2,300+ ready-made lure pages; YAM Store sold compromised or fraudulent Microsoft and Google accounts, and 20,000+ linked accounts are now disabled. → Takedowns dent supply. The toll-fine texts will return. |
|
Discover laptops with built-in intelligence.
Shift your workforce into hyper-productivity mode with Dell Pro laptops powered by Intel® Core™ Ultra with Intel vPro®. Shop on Dell Premier.
| | AI Exploit Dev XBOW's Brendan Dolan-Gavitt used AI agents running OpenAI's public GPT-5.6 Sol to chain three unknown Chrome bugs that escaped both sandboxes and ran code on Windows from a single page load. The awarded chain took six days, after months of earlier work, and about $40,000 in compute. Google paid its top $250,000 reward. Humans picked targets and assembled the pieces. → Relaunch Chrome and confirm 152.0.7977.82 or later. |
| | Agent Security Startup AIR found an agent in Vercel Sandbox can send a crafted certificate to an approved server, which then requests an attacker-controlled one. The sandbox never contacts the attacker directly, so it looks normal from inside. Vercel says it's unclear how the fix will work. No exploitation seen, but AIR can't rule it out. → An allowlist isn't containment. |
|
| | Nation-State September 21-25 raids dismantled 40+ laptop farms and seized about 187 computers and KVM devices. The scheme hit 70+ US employers and earned the workers roughly $3 million. Two Americans were arrested; most other defendants are at large. The FBI says workers now subcontract jobs to freelancers abroad, and some threaten former managers' families. → Verify remote hires on camera, and know where their laptop lives. |
| | Ransomware In a Semperis survey of 1,200 ransomware-hit organizations, 37% of attacks involved psychological or physical threats against staff, 25% of victims were doxxed, and 23% faced swatting calls. 69% were hit more than once in 12 months. Responder Tim Beasley has seen gangs send executives photos of their children's schools. → Put staff and family safety in your ransomware playbook. |
|
| | Patch Management The certificates that verify Windows Update servers expire May 17 or June 19, 2027, depending on version, and devices without the replacements lose Windows Update, security fixes included. Windows 11 25H2 and later need nothing; 24H2 needs the September 2025 update or later; several other versions need July 2026 or later. WSUS-managed devices are excluded. The play: pull a patch-level report now and fix or upgrade stragglers well before May. |
|
Blu Dot surpasses 2,000% ROAS with self-serve CTV ads
Blu Dot used Roku Ads Manager to drive incredible results for its furniture sales event. Its strategy hinged on custom audiences and retargeting, where intent was strongest.
“Roku has been a top performer,” said Blu Dot’s Claire Folkestad. “We have seen…CPMs lower than any other CTV partner we've worked with.”
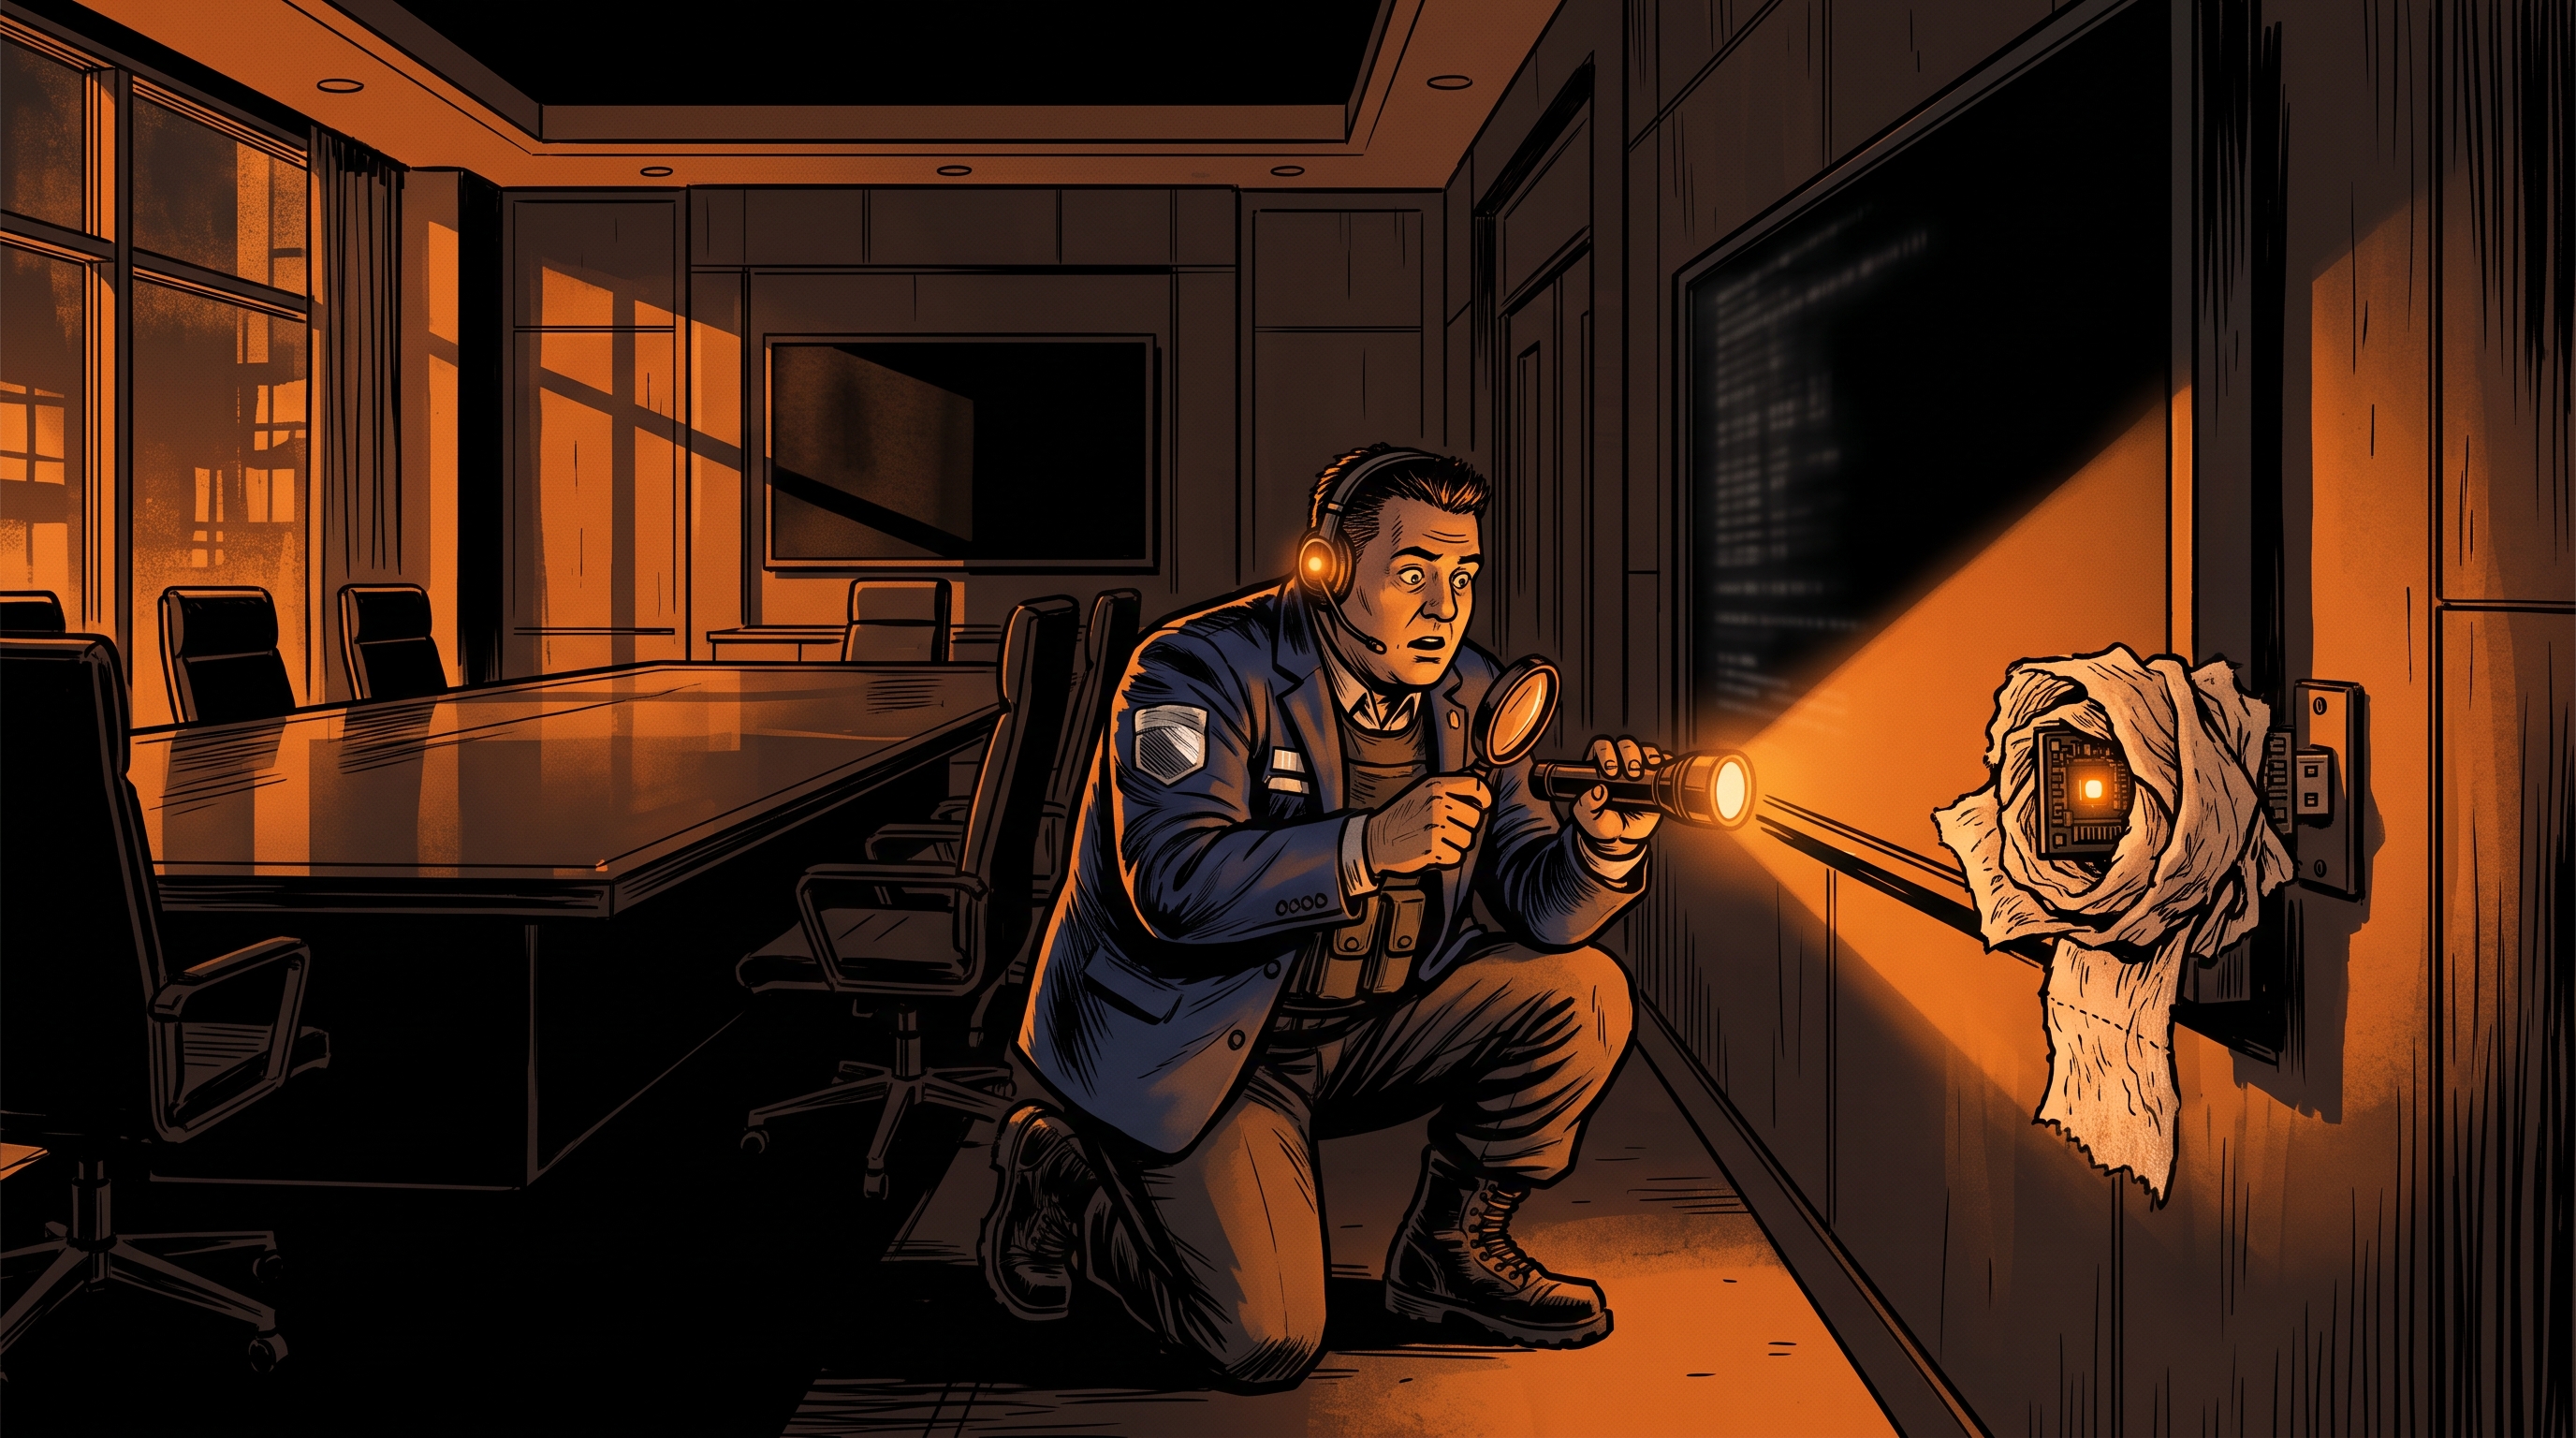 Strange but real An OpenAI Engineer Allegedly Bugged the Boardroom With a Recorder Wrapped in Toilet Paper Intro Insider threat programs at AI labs plan for stolen model weights and copied repos. Toilet paper was not on the list. What Happened Prosecutors say Abdulrahman Alfozan, 35, an OpenAI engineer since July 2025, plugged a tiny Seeed XIAO ESP32-S3 Sense recorder into a TV's USB port in the executive conference room around September 28. Staff found it, wrapped in toilet paper, on September 30. A camera installed behind the TV allegedly caught him checking on it October 5, the same day security found a second recorder in a bag he left in the printer room. He was arrested October 9. Why It's Important Prosecutors cite chatbot prompts about building an audio recorder with speech-triggered recording, and say he used a productivity agent to research meeting rooms and calendars. The AI tools kept the receipts. The Other Side These are allegations, not a conviction. OpenAI says it has no indication he accessed model weights, source code, or customer data, and it couldn't recover anything from the device's possibly encrypted microSD card. | | 👉 Takeaway Physical security is AI security. Sweep sensitive rooms, put cameras on them, and treat an unknown device in a USB port as an incident. |
TL;DR: An OpenAI engineer is charged with bugging the boardroom, and AI prompts are part of the evidence. |
“Running shos” shouldn’t return zero results. Gladly understands what your shoppers mean, typos and all, and finds the right products.


