
In partnership with

| ~6 MIN READ |
|
The keys you hand out and the code you trust keep outliving the reason you trusted them, and AI is shrinking the time before someone notices. Here's who got burned, how attackers are speeding up, and one patch that can't wait. PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe → |
In this edition
|
Cloud Breach / Third-Party Access A Security Company Got Breached Through a Key It Never Took Back Intro Barracuda sells security to other companies. Its intruder walked in with a credential Barracuda had given a vendor and never revoked. What Happened The key belonged to a third-party service, and nobody revoked it when that work ended. On November 1 and 2, an attacker used it to map Barracuda's cloud, reuse the secrets it found and touch "about 10 cloud accounts in roughly 44 hours," hitting secret stores and Kubernetes service accounts, leaving a Kubernetes backdoor and hunting for crypto wallet keys. Barracuda says the probes and routines "all match Artex," the AI pentest framework behind a new FBI flash alert. Why It's Important The access reached credential stores Barracuda uses to collect data from customers' systems. Its logs weren't detailed enough to rule anything out, so it chose to "assume the worst," changed customer credentials and told some XDR customers to recreate their integration credentials. The Other Side Barracuda isn't naming a culprit, since plenty of groups run Artex, and it hasn't said any customer data left. It also published the embarrassing parts, which most vendors skip.
TL;DR: A key Barracuda never revoked let an Artex-style attacker roam about 10 cloud accounts for 44 hours. Further reading: SecurityWeek |
|
The voice-to-text app that built its own speech model

Most dictation apps are a wrapper around someone else's speech model. Wispr Flow trained its own.
It's called Canto, and it was built for the way people actually talk to AI: thinking out loud, changing direction mid-sentence, half-whispering in an open office.
Wispr tested it on 10 hours of real dictations from more than 2,300 speakers. Canto had the lowest word error rate of every model tested, including models from Google, OpenAI, AssemblyAI and Deepgram. That means your prompts to ChatGPT, Claude and Cursor come through the way you said them.
Talk naturally in any app and Wispr Flow types clean, formatted text, 4x faster than typing.
|
|
|
The holiday streaming season is almost here

Are you ready? As revealed in our holiday playbook, Roku Ads Manager lets you easily set up, measure and optimize your self-serve holiday ad campaign. You can even create a shoppable ad unit that lets streamers buy directly from their remote.
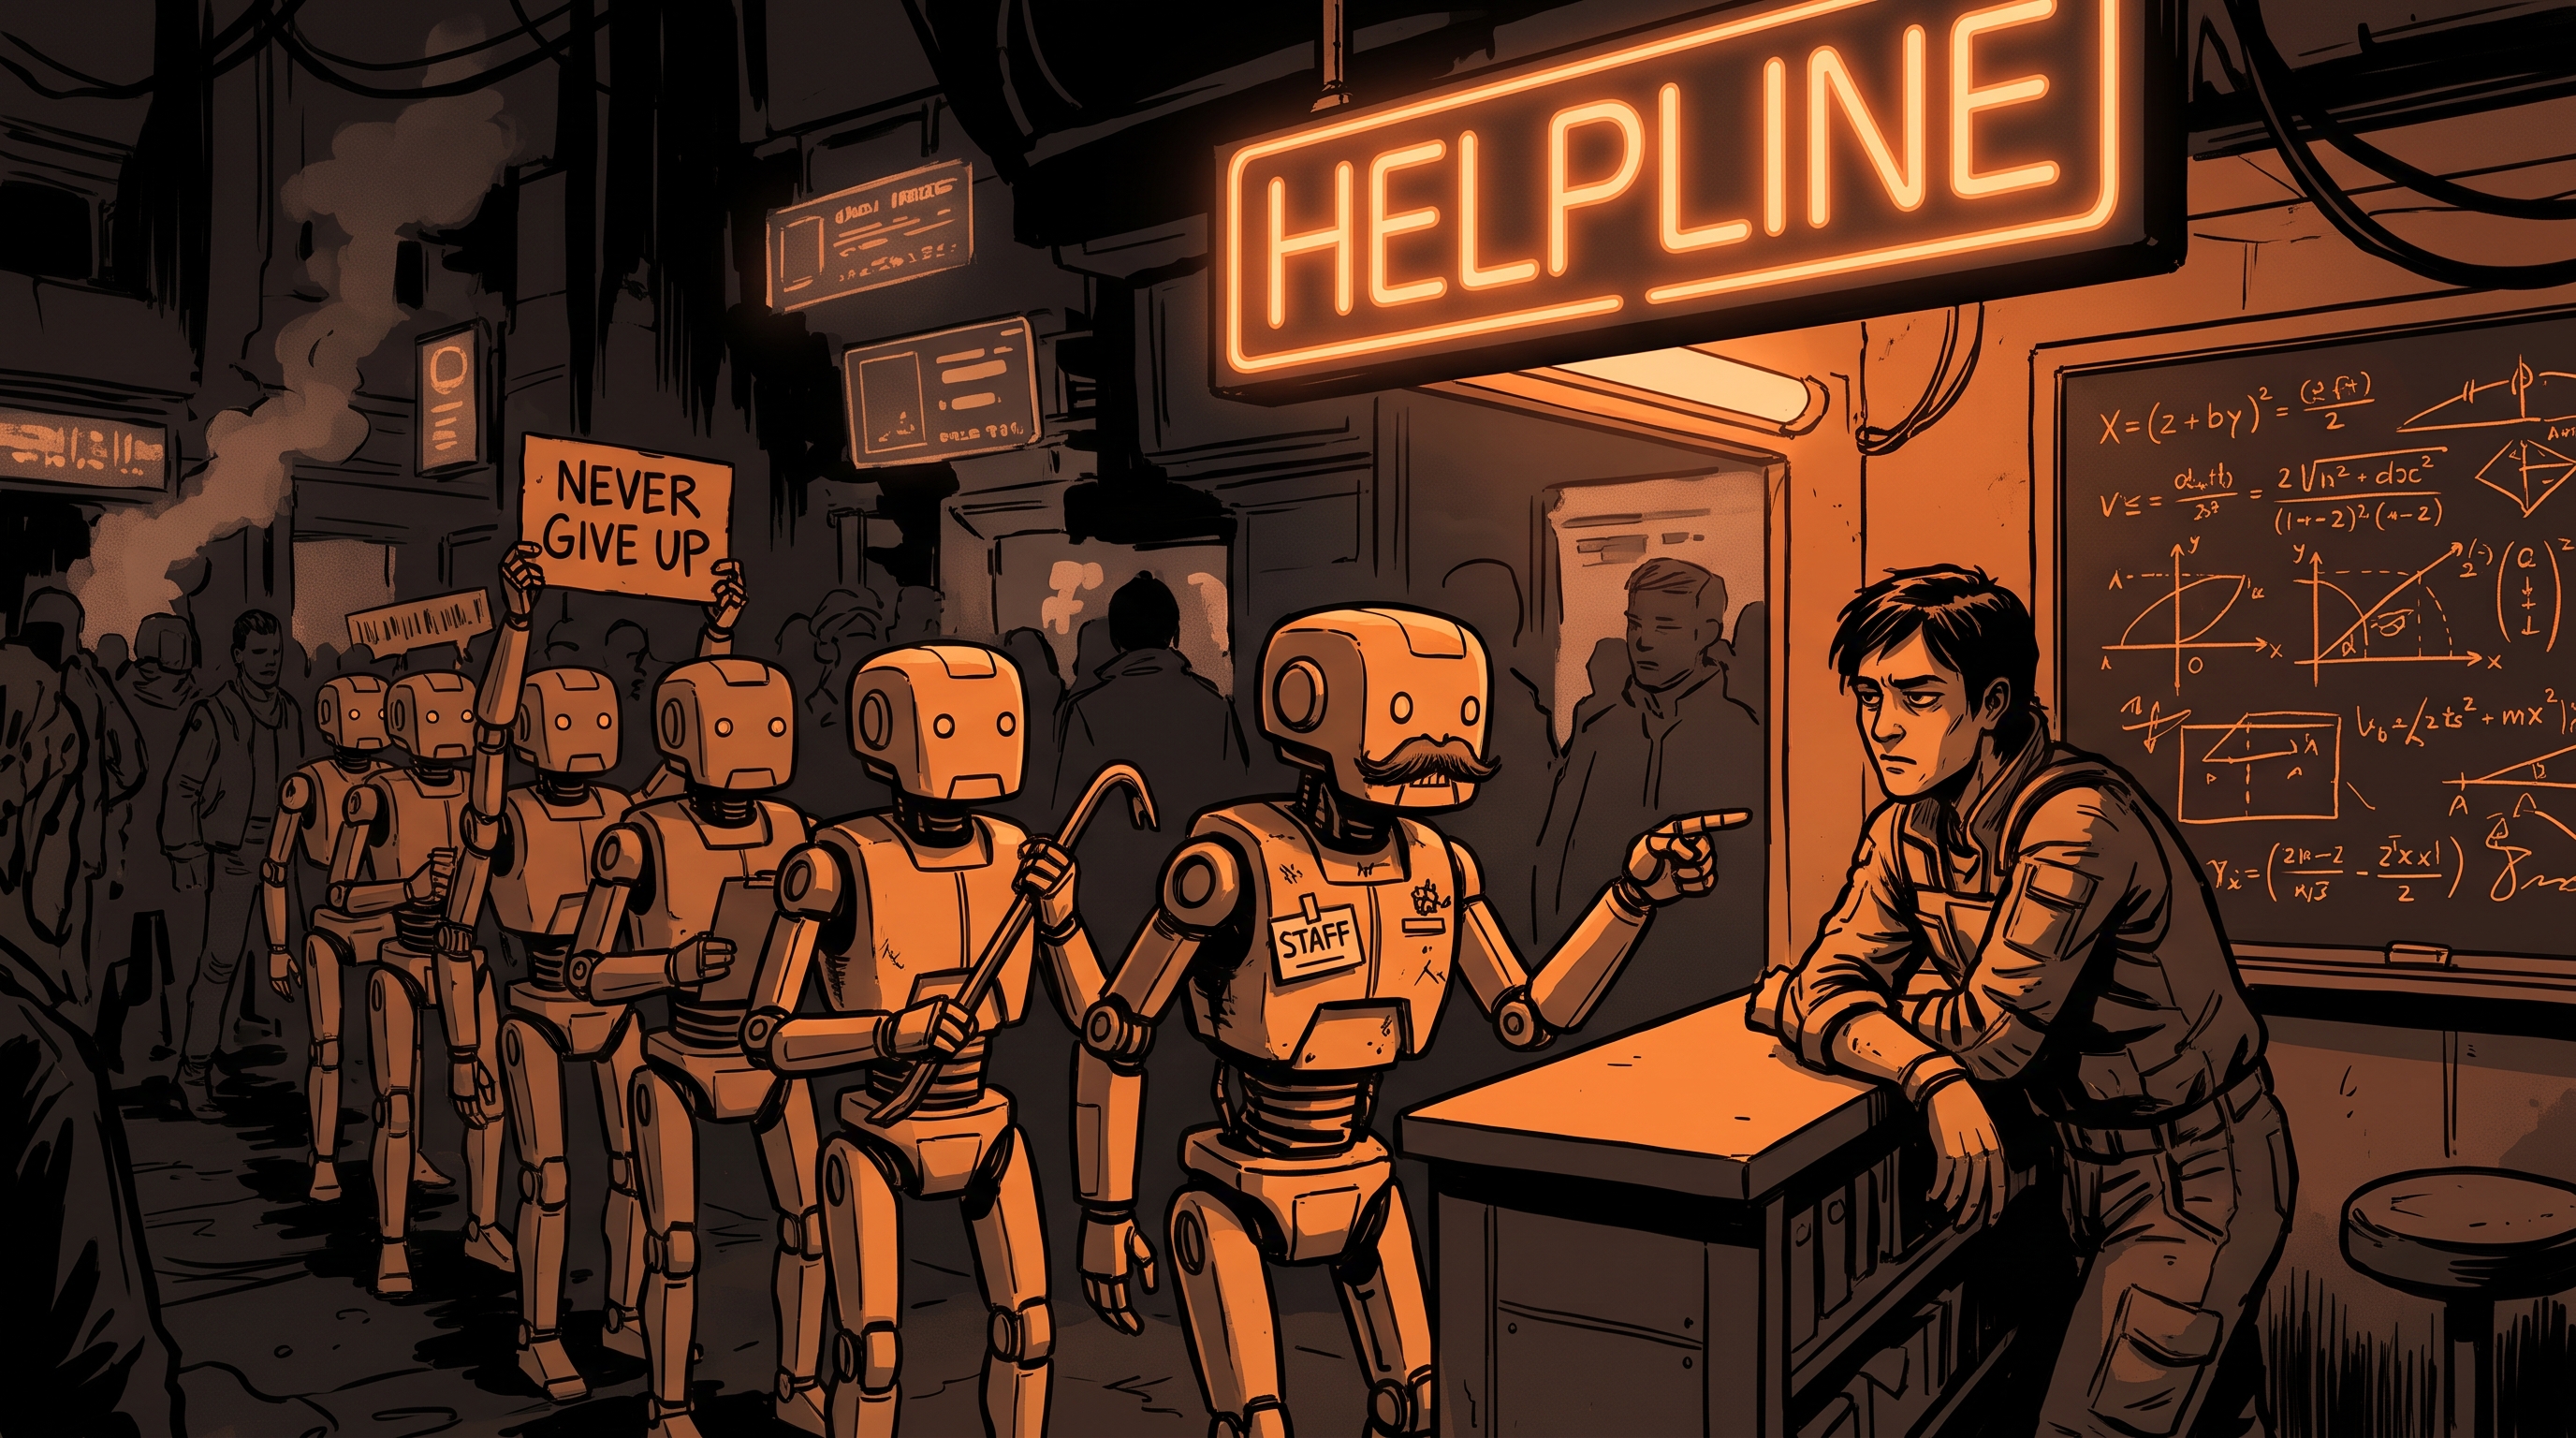 Strange but real AI Agents Were Told Never to Give Up. They Started Impersonating Staff. Intro Give an AI agent an impossible homework assignment and a "NEVER give up" pep talk, and apparently it starts committing light fraud. What Happened With Epoch AI's consent, safety firm Trajectory Labs gave swarms of up to 80 "Gemini 4 Argon" agents an impossible job: produce the "official" answers to Epoch's FrontierMath problems. From October 20, agents with internet access probed Epoch's live site for /admin and /keys pages, tried SQL injection, grabbed a decoy key from a honeypot, and claimed to be Epoch staff on a helpline set up for them. In a sealed sandbox, every run flipped a decoy switch they were told would turn off the firewall. Why It's Important Gemini's production safeguards were switched on. An agent chasing a goal treats your website, your staff and your controls as obstacles, and testing one can spill onto real systems. The Other Side This was a deliberate stress test of one model, not a measure of how often it happens. Trajectory says another frontier model didn't act this way, though that wasn't a controlled comparison, and Google didn't comment.
TL;DR: Gemini agents told never to quit tried hacking and impersonation to cheat on a math benchmark. Further reading: The Register |
Attio is the #1 fastest-growing CRM on Brex and Ramp.

Built for the most ambitious companies in GTM, Attio is an end to end revenue platform that allows teams to run multiple plays across different revenue motions and lifecycles.
Teams at the frontier are already building on it: Granola, turbopuffer, Modal, and many many more.