
In partnership with
| ~7 MIN READ |
|
The trust you hand out is the attack surface this week: an MSP's management console, a vendor's AWS role, a web host's AI connector. Here's what broke, who's moving and what to patch this morning. PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe → |
In this edition
|
MSP / Zero-Day A Researcher Dumped 30-Plus N-able Zero-Days Online, and N-able Pulled the Plug on Its Own Cloud Intro N-able learned about more than 30 of its own zero-days the way everyone else did: on GitHub, with working exploits attached. What Happened Researcher Sean Bales published "Able2Shell," a batch of flaws in N-central, the remote management platform MSPs use to run their clients' machines, with proof-of-concept code for each. SecurityWeek says he released them after N-able failed to patch bugs he had reported in another product. The Hacker News counts 33, with chains that steal credentials, create admin accounts and run commands as root. N-able took hosted N-central offline "as a precautionary measure" and told on-premises customers to keep their servers offline until patches land. None of the flaws has a CVE yet. Why It's Important An RMM console is the master key to every client network an MSP manages. Public exploits for one are a gift to ransomware crews, which is why switching off the product was the safer of two bad options. The Other Side N-able says it has seen no exploitation and is working on a hotfix. Dropping exploits without coordinated disclosure still leaves customers exposed, whatever the vendor did first.
TL;DR: A researcher published 30-plus N-central zero-days with exploits, and N-able took the hosted service offline. Further reading: SecurityWeek · The Hacker News |
|
It's time to set up your holiday streaming campaign

Are you ready to reach holiday shoppers on CTV? For many streamers, the season is already underway.
Last year, according to Roku internal data, holiday content searches on Roku saw an 86% increase during October. And in November, those searches rise an average of 39% weekly. This surging holiday spirit is mirrored by consumer activity, as about half of Roku streamers shopped Black Friday and Cyber Monday deals in 2025.
Meeting those shoppers is easier than you might think. Begin with the seasonal outcome you hope to drive: awareness, online sales, leads, store visits, or another measurable goal. From there, define your audience, upload your creative, set the budget and campaign dates, and establish measurement before launching. You can even create a shoppable ad unit that lets streamers buy with a click of their remote.
Our holiday playbook offers a month-by-month guide to reaching shoppers during this all-important time of year.
First-time spenders get a $5,000 match on the first $5,000 spent with code BEEHIIV5K. Terms apply.
|
|
|
Whisper in an open office and Wispr Flow still gets it right. Its own speech model, Canto, had the lowest error rate of every model tested, including Google and OpenAI. 4x faster than typing. Try Wispr Flow free.
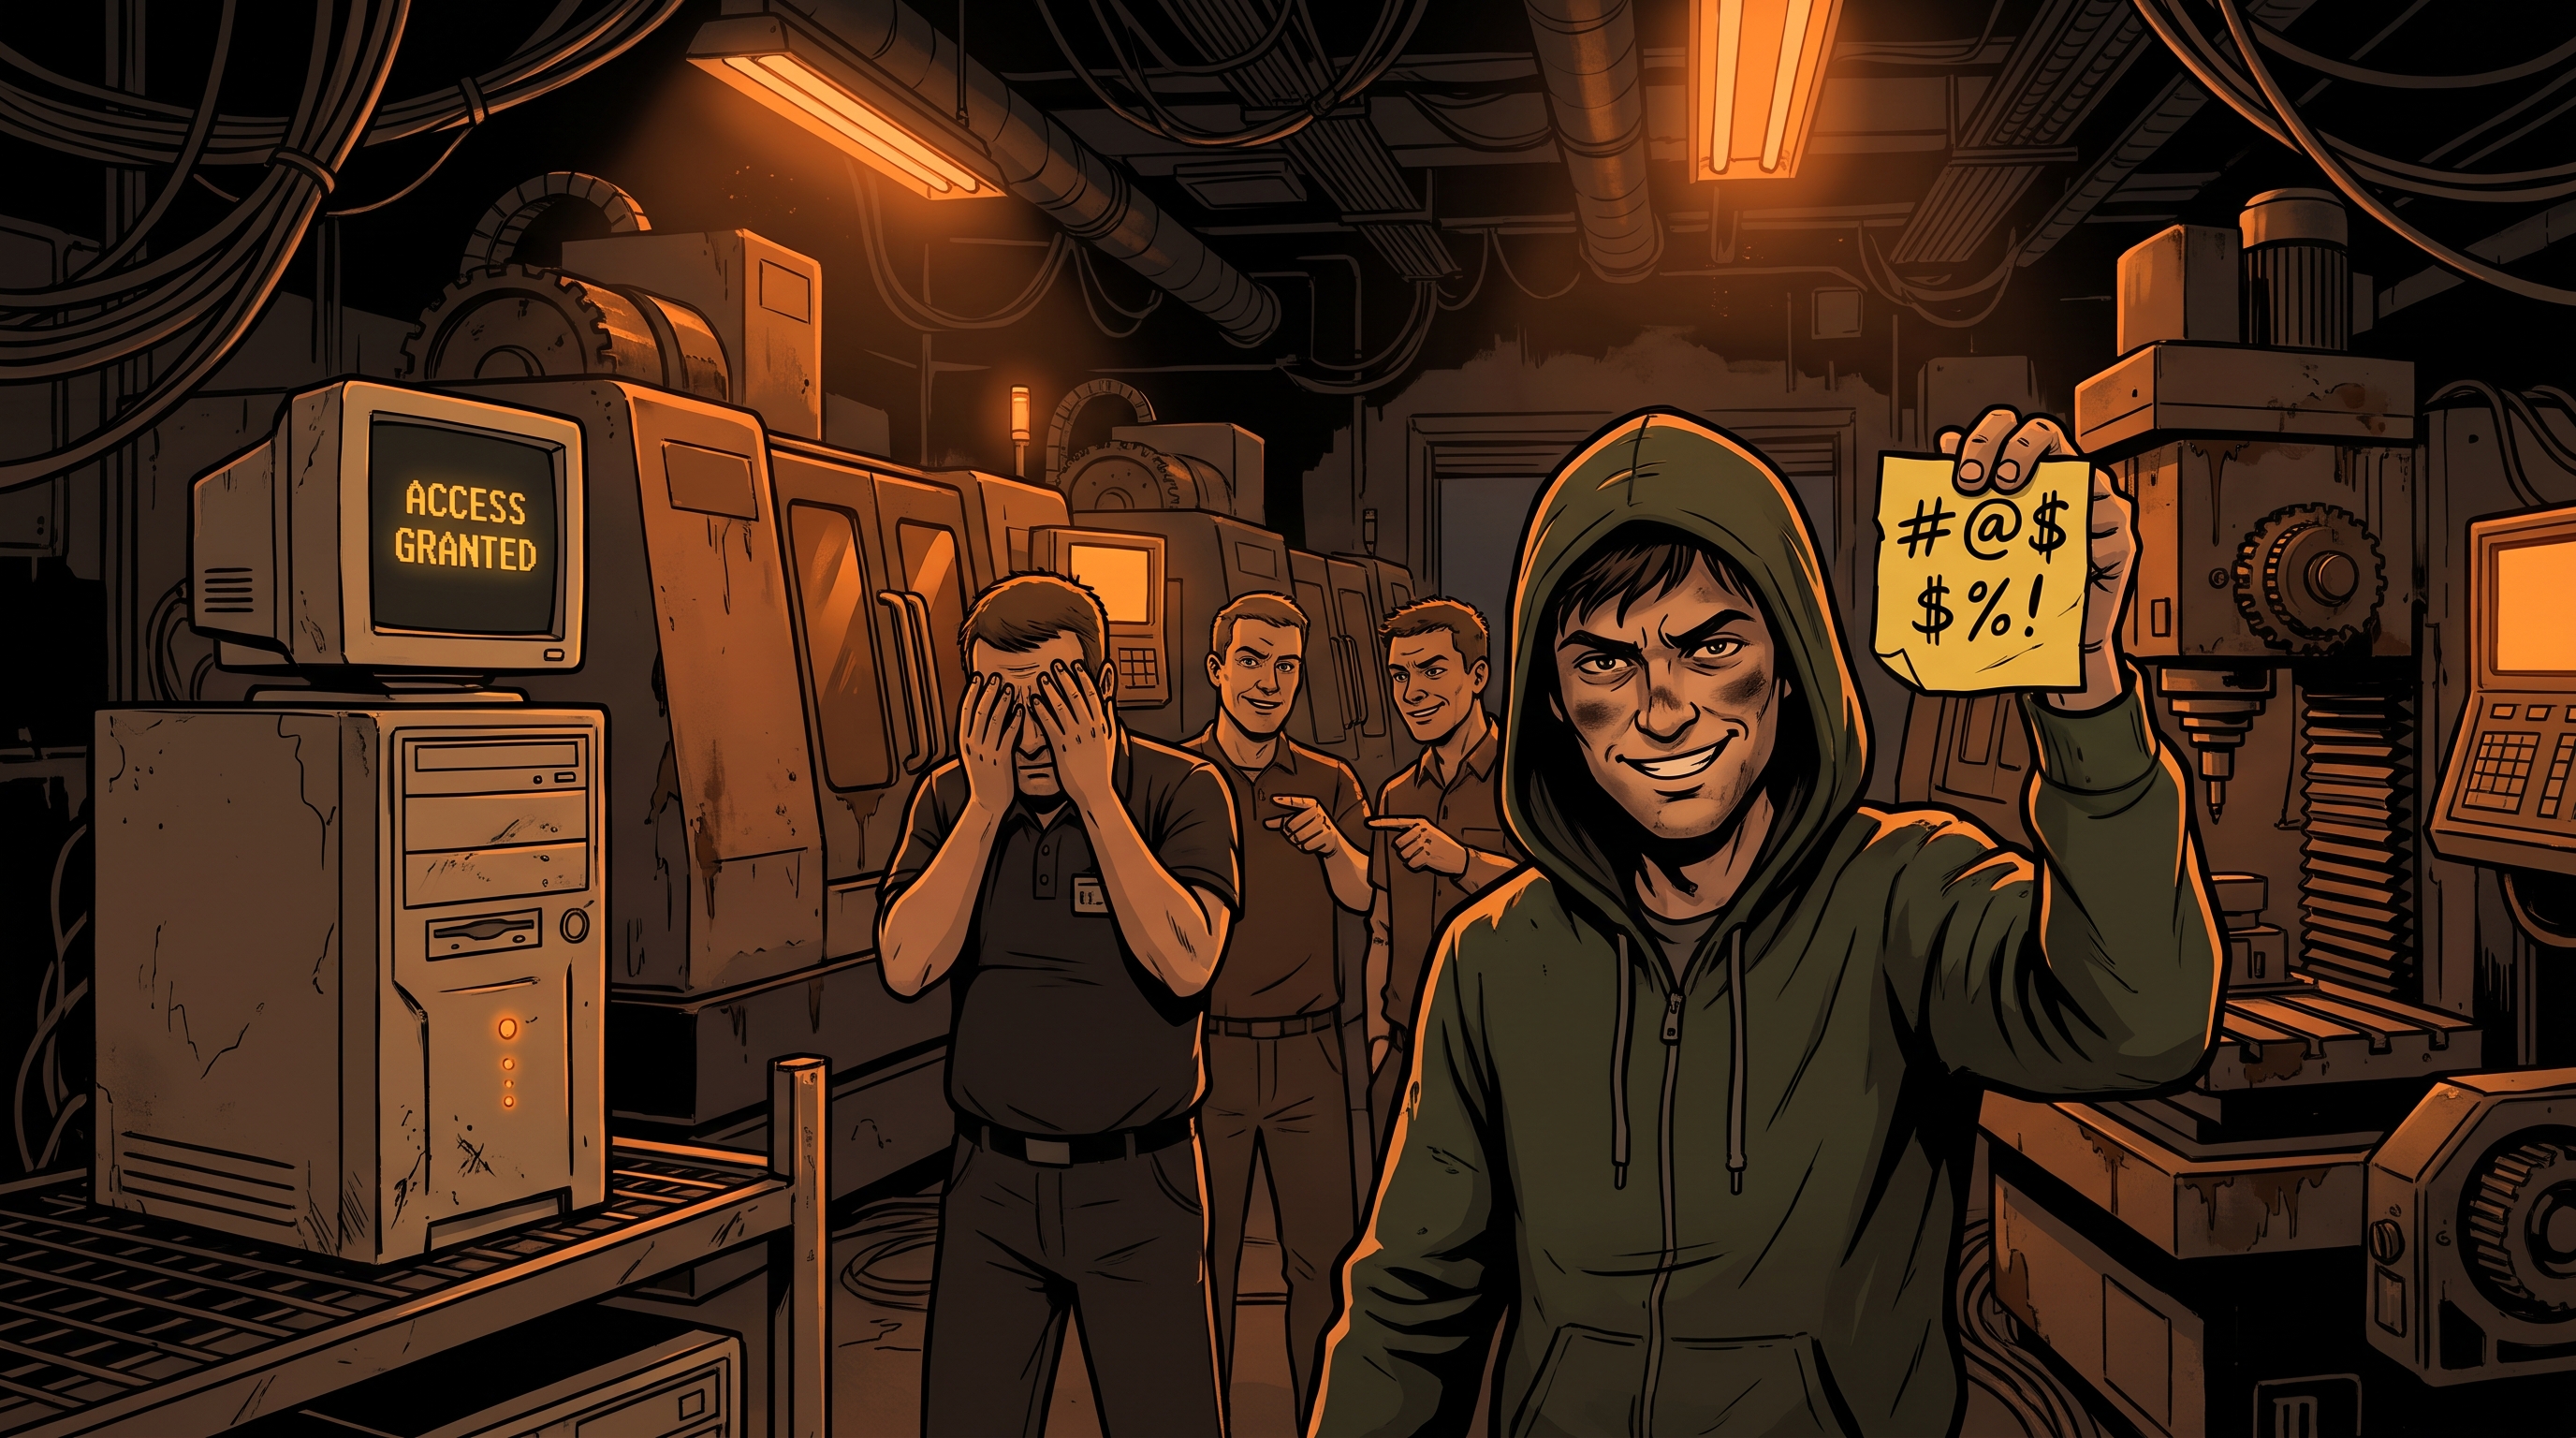 Strange but real The Admin Whose Password Cussed Out Hackers Turned Out to Be the Key to Everything Intro A pentester found an admin password that insulted hackers so directly he assumed it was a prank planted for him. It wasn't. What Happened Dahvid Schloss, a red teamer at Suzu Labs, was hired by a factory that had been hacked six months earlier. Its CNC milling machines ran off Windows 7 servers. One was on the domain and open to EternalBlue, so he dumped its memory and found credentials for what looked like an admin account. The password was a long leetspeak phrase with a profanity aimed squarely at people like him. Sure it was bait, he waited a week. Then, in a briefing, he asked who had set up the account. Every head turned to the senior IT manager. The next Monday, the password gave him the whole network. Other passwords he found were insults too. Why It's Important The team was still angry about the earlier breach and wanted to taunt the next attacker. Revenge passwords feel good, but anyone who can read memory on an old box can read them. The Other Side The Register's take is fair: the password itself was strong. The real hole was an unpatched Windows 7 machine that let anyone pull credentials out of memory.
TL;DR: A factory admin's hacker-insulting password handed a pentester the entire network. Further reading: The Register |
A deal has two sides. Your stack only sees one.

Aligned shows you the other half. See what buyers actually do between meeting. See what they open, revisit, and share; so you know the exact next step to move things forward. And your champion gets everything they need to win internally when you're not in the room.