
In partnership with
| ~6 MIN READ |
|
This week's break-ins came through the side doors: add-ons, hijacked developer accounts and a government mail server that doubled as a spy's base. Here's what got opened, who's behind it and what to patch before the weekend. PS: Was this forwarded to you? Subscribe free at exzeccyber.com/subscribe → |
In this edition
|
MSP / Supply Chain 288 Computers in 90 Minutes, All Through One ScreenConnect Add-On Intro Nobody had to break ScreenConnect itself this time. The intruder came in through an add-on bolted onto it. What Happened Huntress says someone used several cloud-hosted ScreenConnect panels to push rogue copies of the remote access tool onto 288 computers at 48 organizations within about 90 minutes. It traced the activity to RMM+, an independent extension that skips ScreenConnect's accounts, roles and MFA for a shared access key, blank by default in two versions. The toolkit, SCKit, also tried replaying stolen session cookies against other customers' panels. ConnectWise disabled RMM+ and four other extensions in about 400 partner environments; on-premises customers have to do it themselves. Why It's Important One remote management panel reaches every client an MSP manages, so an add-on that sidesteps MFA works like a skeleton key. Blackpoint says the kit also exploits CVE-2026-84869, September's 9.9 ScreenConnect flaw, which hits clients that were never patched. The Other Side ConnectWise says it found no compromise of its infrastructure and no flaw in ScreenConnect itself, and the cookie replays failed in every log Huntress checked. How the intruder first reached the panels is still unknown, and nobody has been named.
TL;DR: A third-party ScreenConnect add-on let an intruder plant rogue remote access at 48 organizations. Further reading: The Record · CyberScoop |
|
Are your sales foundations ready to scale?

You’re growing from 10 reps to 100. Your agents can only work with the data and processes you give them, and the foundations you set now decide whether your systems hold.
Attio’s agentic sales audit looks at where you are today and shows you where to start, whether that’s your data foundation or a fuller agentic sales process.
|
|
|
See what's really happening in every deal

Aligned shows you what buyers are doing between meetings inside your most important deals then surfaces the risks, openings, and next steps. No more guessing where a deal stands or finding out a champion went quiet too late. Just real visibility, so you can act before it's too late.
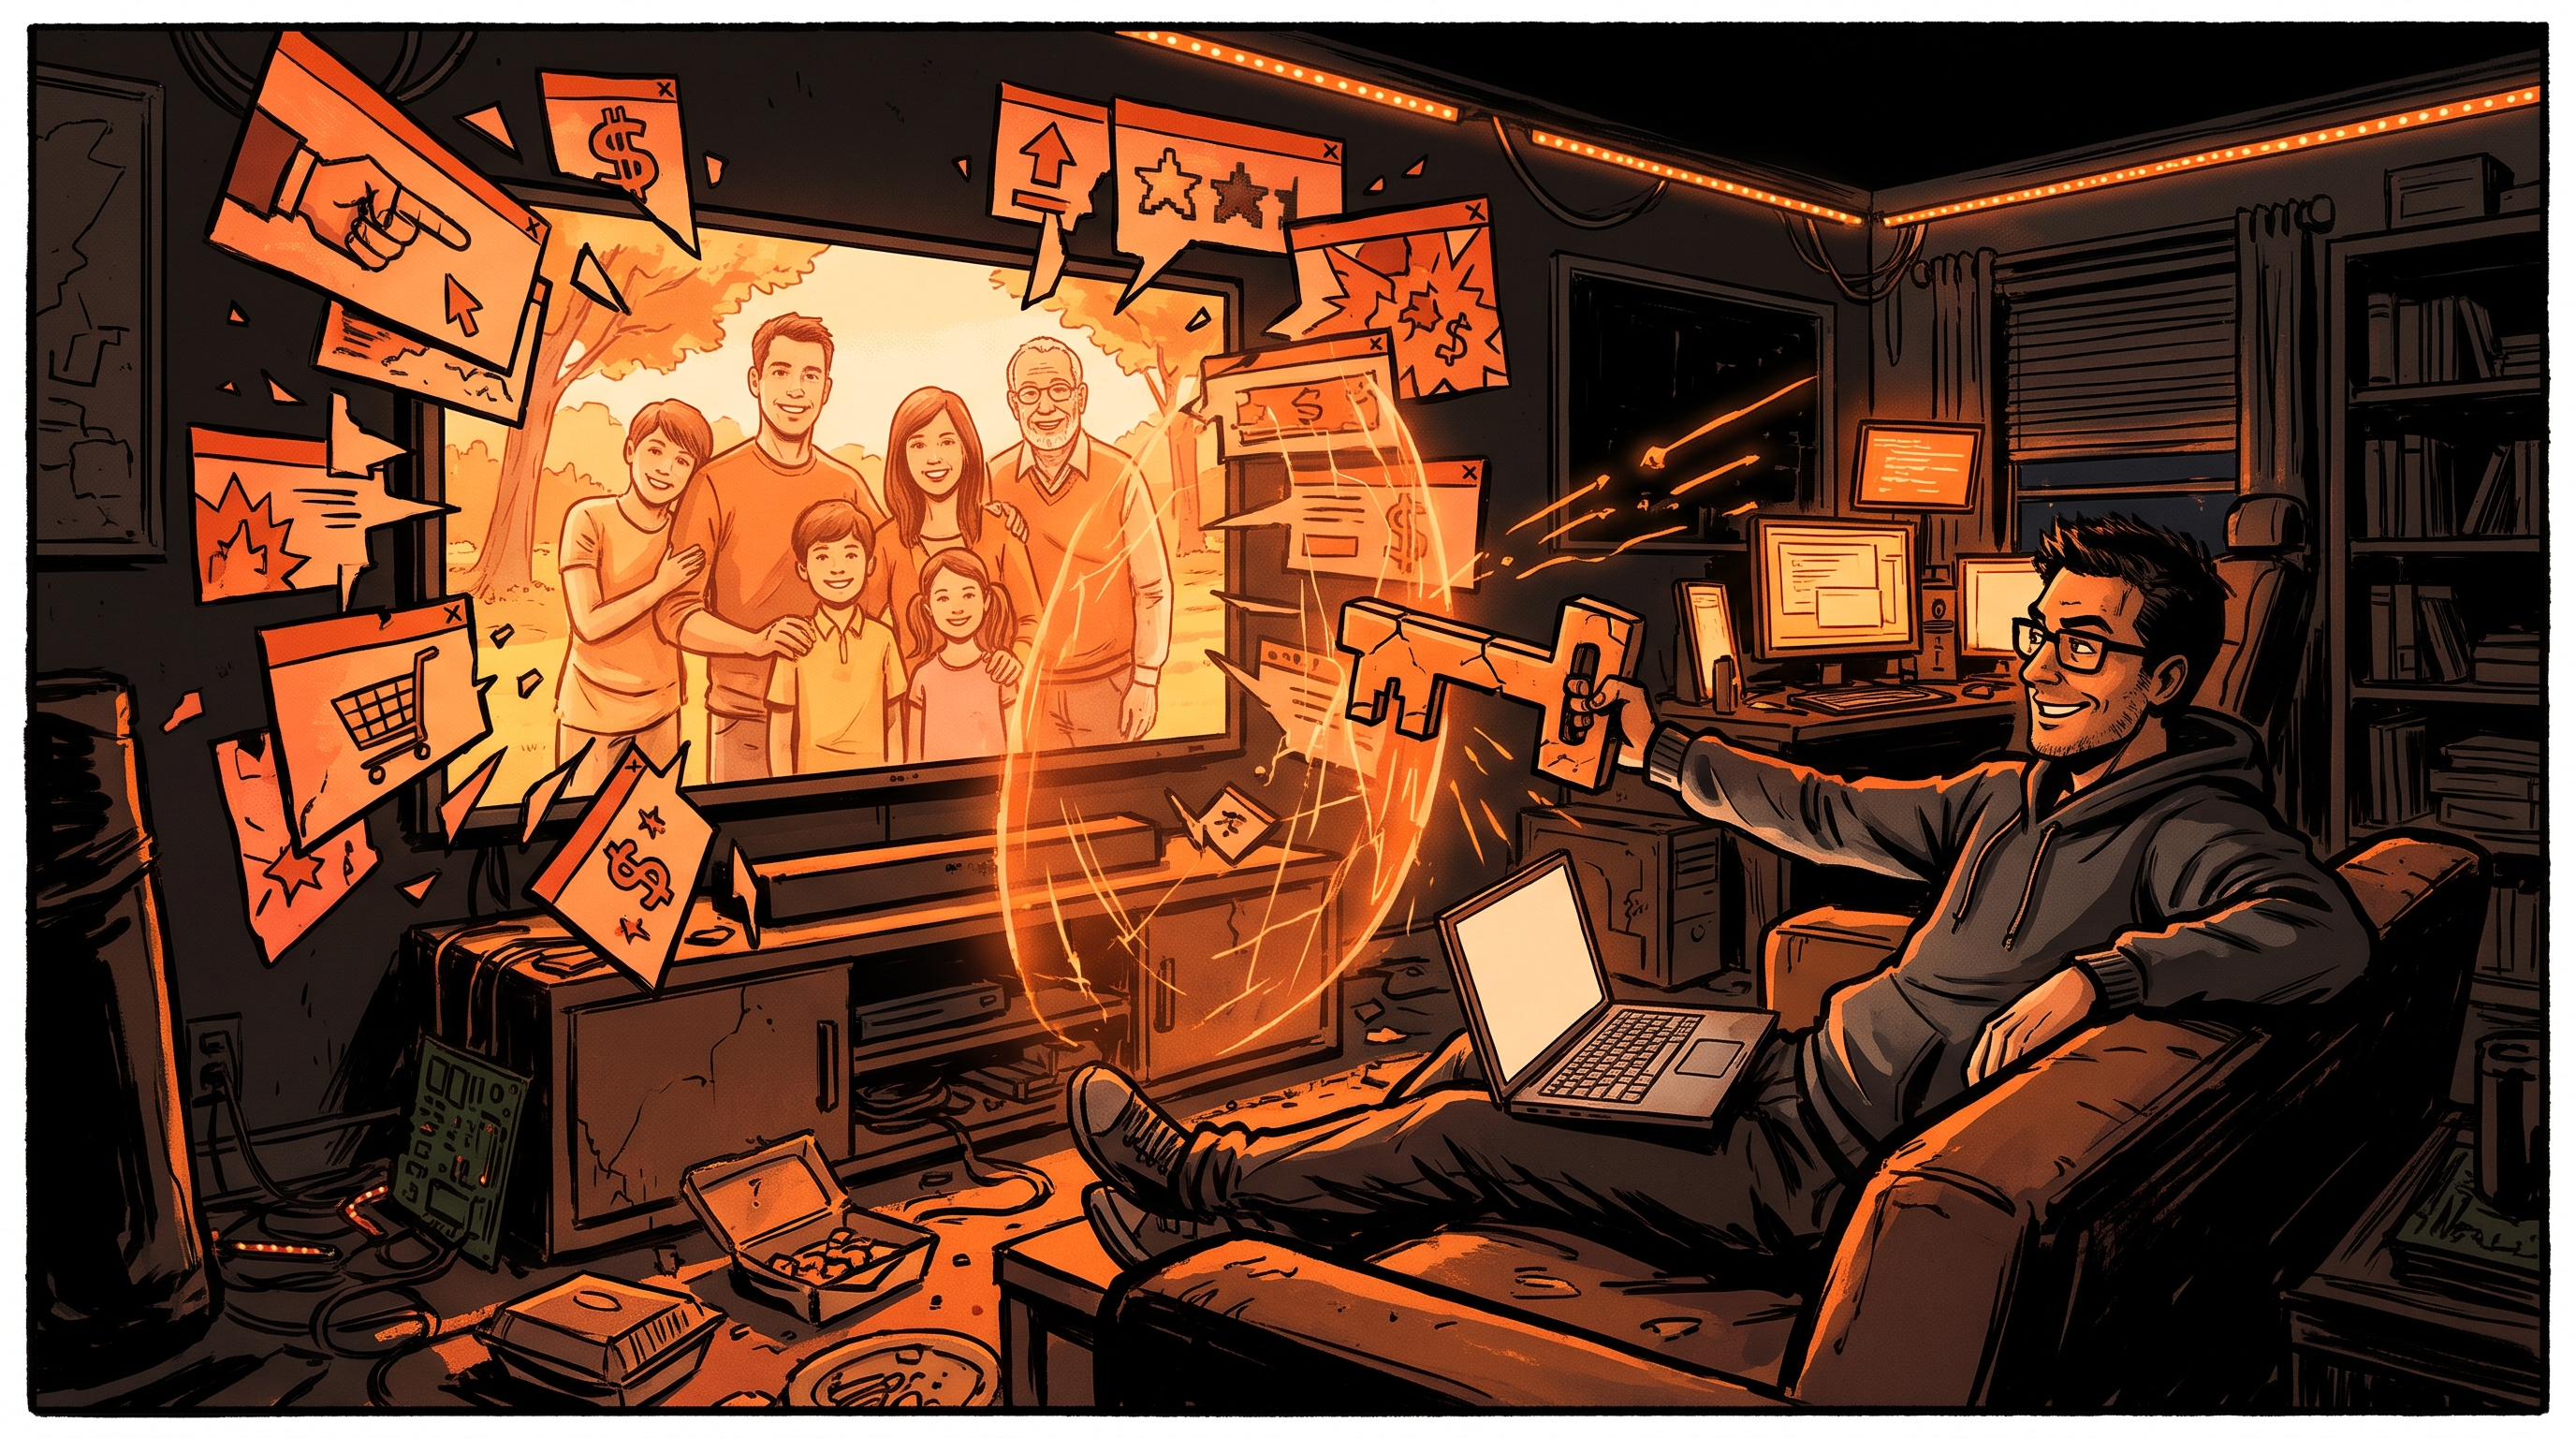 Strange but real A Programmer Used a Broken Certificate Authority to Swap His TV's Ads for Family Photos Intro Most people mute the ads on their smart TV. Daniel Vrátil replaced them with pictures of his family, using a certificate authority's busted keys. What Happened Indian CA eMudhra, which says it issued more than 60 million certificates, had eight intermediate keys that turned out to be weak; one of them was the number four. Vrátil, a Czech developer, fed those keys to mitmproxy, minted certificates for Samsung's ad servers and pointed his 2022 Samsung TV at a box on his home network. Ad requests now get family photos from his NAS, and tracking calls get dropped. It works because Samsung hadn't shipped firmware that stops trusting the bad certificate. He posted it on GitHub as samsung-tv-adspoofer. Why It's Important A device that still trusts a broken CA will believe anyone holding its keys. Vrátil says the same trick could serve "countless much more sinister applications." The Other Side In his words it's "not exactly a one-click setup," and a Samsung update that revokes the certificate ends it. eMudhra has left the certificate business and blamed a buggy key-generation script.
TL;DR: A developer used eMudhra's broken CA keys to swap his Samsung TV's ads for family photos. Further reading: The Register |
Watch on demand: Tabs + PwC break down how finance teams are operationalizing usage-based pricing — without the manual overhead.